Dev tools · alternatives · 2026
24 alternatives to Code in Response to “The Trouble with Symlinks.”
See: https://news.ycombinator.com/item?id=32190032 This was written in about the past hour or so; it has no documentation or test cases yet. Think twice before relying on it in production. The idea is that we can perform a detailed validation of the trustworthiness of an absolute or relative path, as a simple function that can be reused anywhere: I call this function safepath_check. A trustworthy path is one whose meaning cannot be changed by a third party: another user who isn't root. The path is therefore immune, for instance, to TOCtoTOU security problems, like the…
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes. Prices are shown for the 1 we have checked on their own sites. Code in Response to “The Trouble with Symlinks.” launched in 2022; newer entries below may have overtaken it.
- 1

Inspect and refine PATH environment variable on Windows, Linux and MacOS. - epogrebnyak/justpath
2024 · github.com · its alternatives →
- 2

TRUST – Coding Rust like it's 1989. Contribute to wojtczyk/trust development by creating an account on GitHub.
May 2026 · github.com · its alternatives →
- 3
 TrustedRouterpaid▲157
Every model with a unified interface. Privacy with proof.
Aug 2026 · trustedrouter.com · its alternatives →
- 4

- 5CS
The pattern of downloading and executing installation scripts without verifying them has bothered me for a while. I started messing around with a way to verify the checksum of scripts before I execute them. I've found it a really useful tool for installing things like Rust or Deno. It's written entirely as a shell script, and it's easy to read and understand what's happening. I hope it may be useful to someone else!
2022 · checksum.sh · its alternatives →
- 6

We needed something like --dangerously-skip-permissions that doesn’t nuke your untracked files, exfiltrate your keys, or install malware. Claude Code's permission system is allow-or-deny per tool, but that doesn’t really scale. Deleting some files is fine sometimes. And git checkout is sometimes not fine. Even when you curate permissions, 200 IQ Opus can find a way around it. Maintaining a deny list is a fool's errand. nah is a PreToolUse hook that classifies every tool call by what it actually does, using a deterministic classifier that runs in milliseconds. It maps commands to action types…
Mar 2026 · github.com · its alternatives →
- 7
 Mpath▲2
Validate SAN multi-pathing with absolute confidence.
Jun 2026 · mpath.superstack.in · its alternatives →
- 8

- 9

- 10

A Rust crate for containing memory leaks and fragmentation - brannondorsey/mem-isolate
2025 · github.com · its alternatives →
- 11

This past quarter has been awash with sophisticated npm supply chain attacks like [Shai-Hulud](https://www.cisa.gov/news-events/alerts/2025/09/23/widesprea...() and the [Chalk/debug Compromise](https://www.wiz.io/blog/widespread-npm-supply-chain-attack-b...). This CLI helps protect users from recently compromised packages by only downloading packages that have been public for a while (default is 90 days or older). Install: npm install -g @dendronhq/safe-npm Usage: safe-npm install react@^18 lodash How it works: - Queries…
Nov 2025 · github.com · its alternatives →
- 12

Prove that you said things before anyone else
Jun 2026 · yousaidthat.org · its alternatives →
- 13

Hi everyone, I built a runtime to isolate untrusted code using wasm sandboxes. Basically, it protects your host system from problems that untrusted code can cause. We’ve had a great discussion about sandboxing in Python lately that elaborates a bit more on the problem [1]. In TypeScript, wasm integration is even more natural thanks to the close proximity between both ecosystems. The core is built in Rust. On top of that, I use WASI 0.2 via wasmtime and the component model, along with custom SDKs that keep things as idiomatic as possible. For example, in Python we have a simple decorator:…
Feb 2026 · github.com · its alternatives →
- 14

2014 · github.com · its alternatives →
- 15

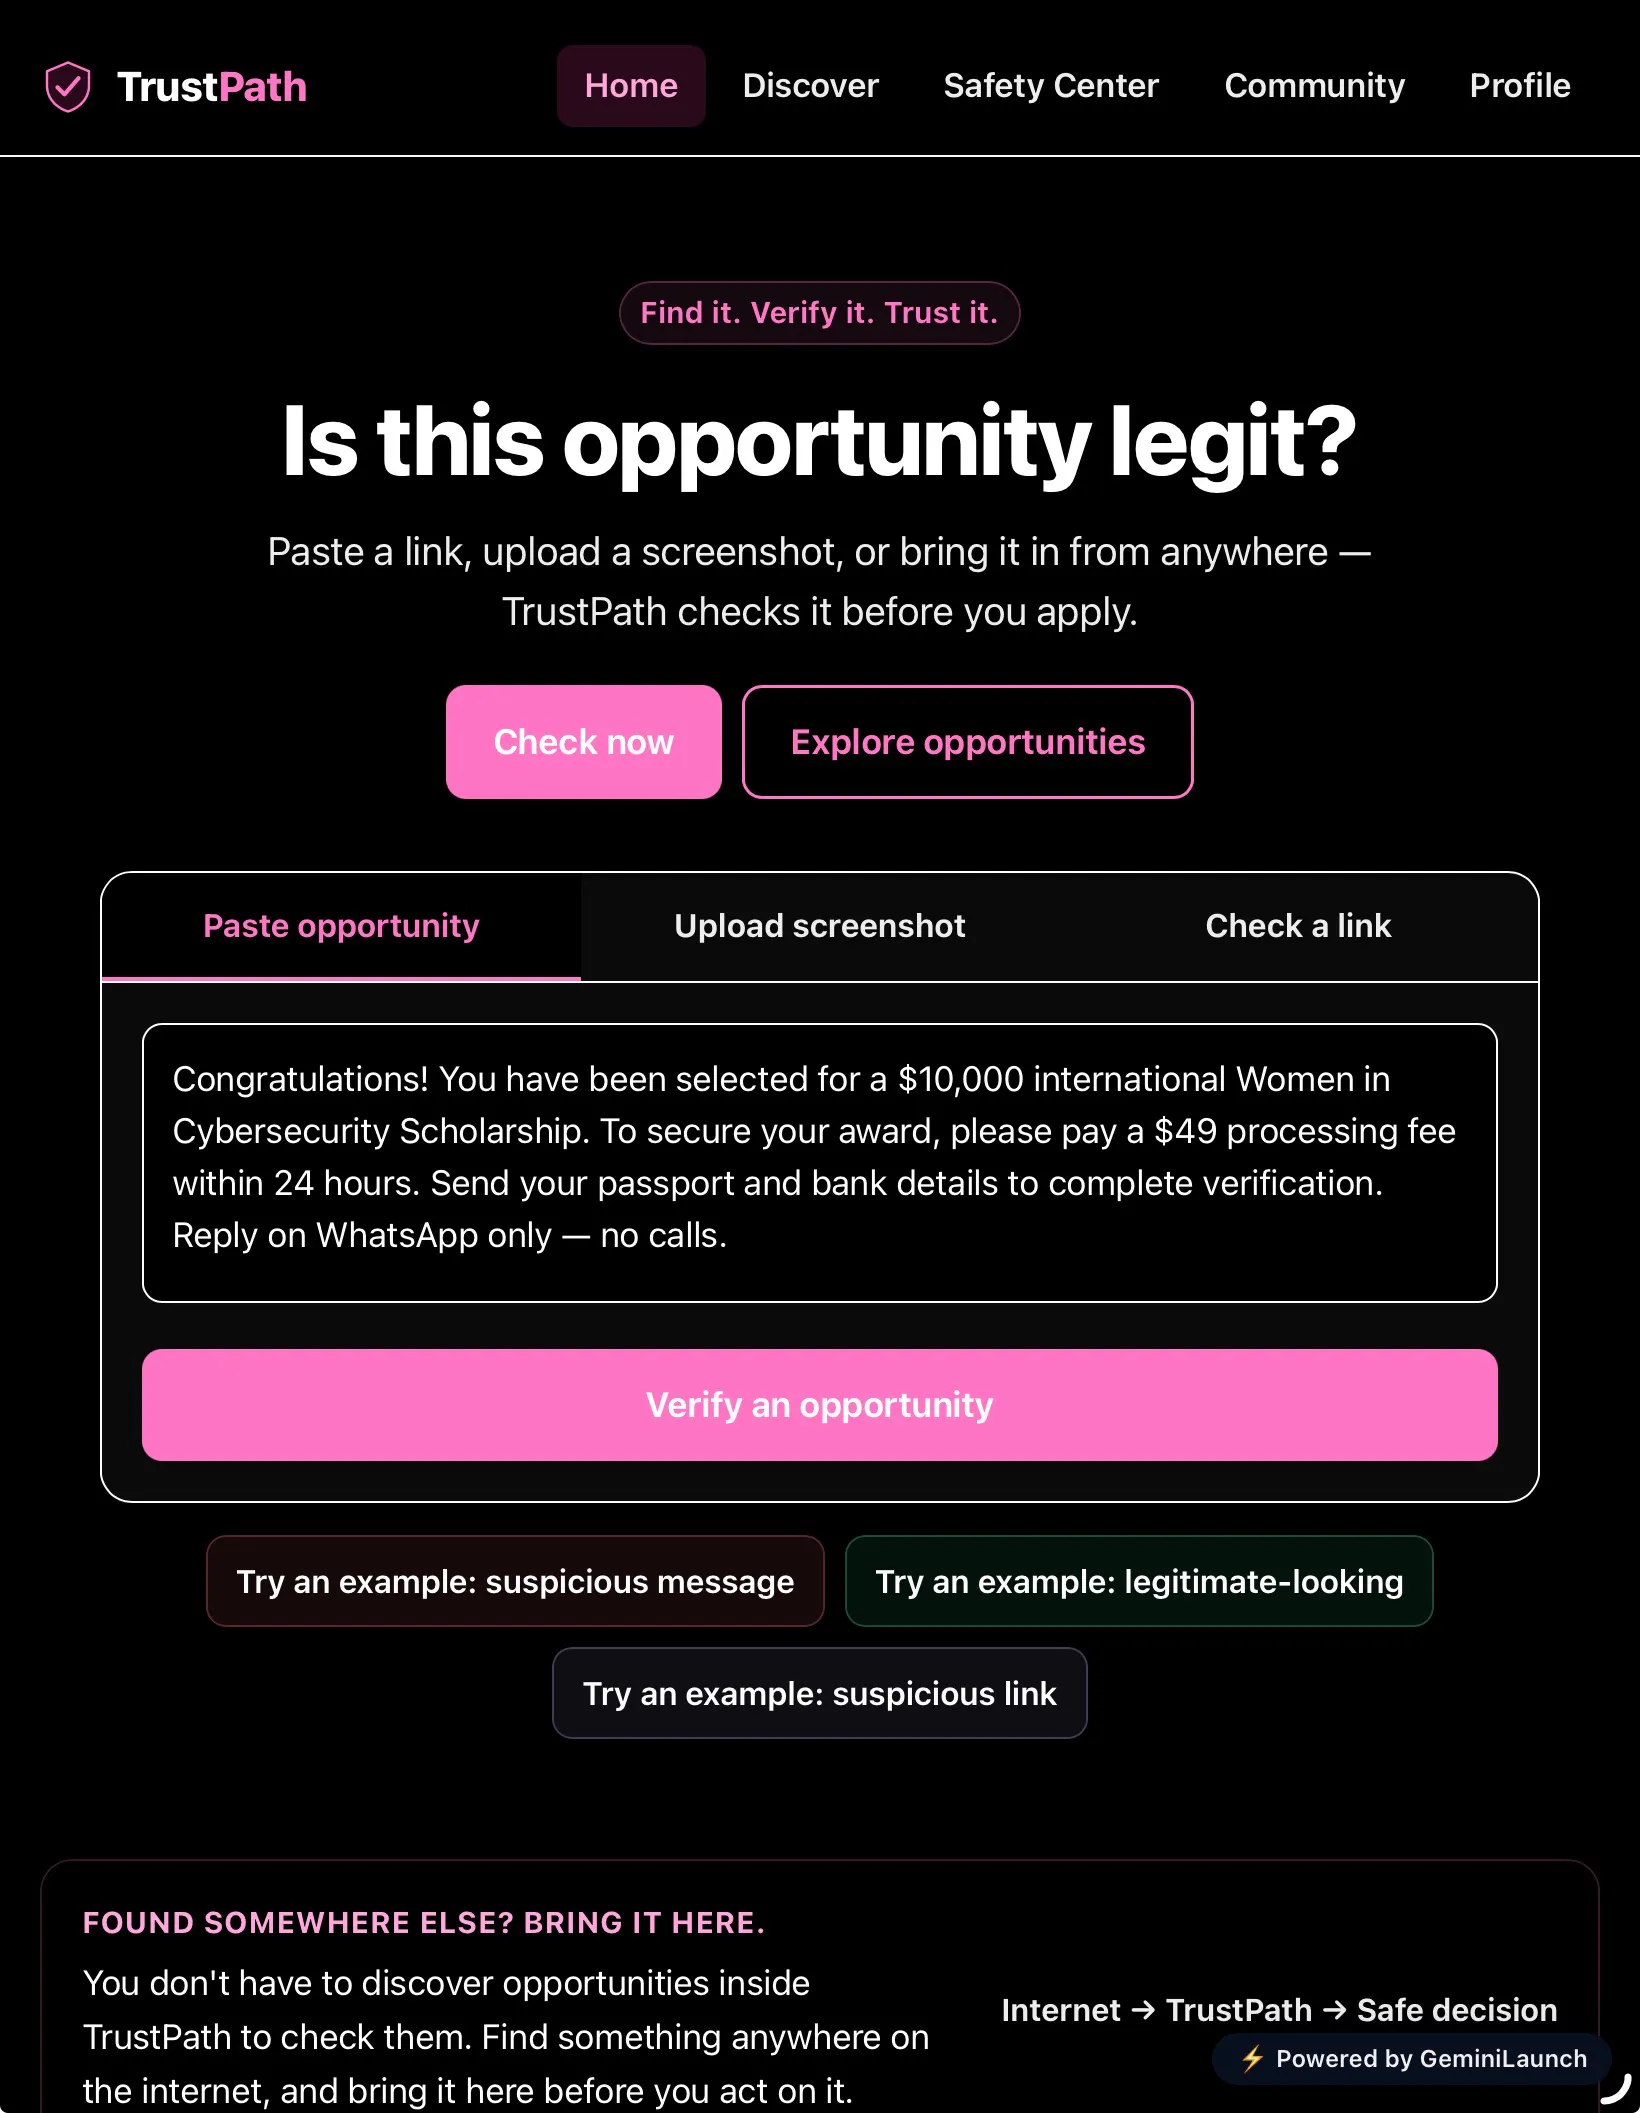
Protect your business with TrustPath's advanced fraud prevention platform. Real-time detection, device intelligence, and comprehensive account protection.
2025 · trustpath.io · its alternatives →
- 16TD
Trusty - Search for an open source package to understand its trustworthiness based on activity, provenance, and more. Brought to you by the founders of projects such as Kubernetes and Sigstore. Hey, Luke here the CTO of stacklok. This is an early experimental preview of Trusty. We use statistical analysis to observe millions of packages and found that Malware typically follows certain patterns. We found this tool really useful to help understand the packages we our pulling into our software and wanted to share it with others. It's still early in and we have a lot more features that will be…
2023 · trustypkg.dev · its alternatives →
- 17

I built a GitHub app that detects it in pull requests, notifies or blocks them. Alongside it, I published a Semgrep ruleset for any stage of the CI/CD. I started this after getting frustrated by all the FUD around malicious code - lots of noise, little effort to solve it. Having said that, it's still a major attack vector - a stored RCE, with the codebase itself as the sink. Feedback is appreciated. The app, PRevent - https://github.com/apiiro/PRevent The ruleset: https://github.com/apiiro/malicious-code-ruleset The research:…
2025 · github.com · its alternatives →
- 18
Instantly check if a website is safe and trustworthy [free].
2025 · scamai.com · its alternatives →
- 19

Check your wheels have the right contents. Contribute to jwodder/check-wheel-contents development by creating an account on GitHub.
2020 · github.com · its alternatives →
- 20

Easily check your website for broken and malicious links. Find and fix 404 errors, mistyped URLs, invalid SSL certificates, or links to questionable websites.
2011 · drlinkcheck.com · its alternatives →
- 21
- 22

In light of the ongoing npm supply chain compromises, I built safe-install: https://www.npmjs.com/package/@gkiely/safe-install It brings a couple of protections I wanted from npm but are not built in. Similar to Bun’s trusted dependencies, it lets you disable install scripts by default and define a list of dependencies that are allowed to run build/install scripts: https://bun.com/docs/guides/install/trusted It also supports blocking exotic sub-dependencies, similar to pnpm’s `blockExoticSubdeps` setting:…
May 2026 · npmjs.com · its alternatives →
- 23

ValidKube combines the best open-source tools to help ensure Kubernetes YAML best practices, hygiene & security.
2022 · validkube.com · its alternatives →
- 24

Linux Foundation survey says 70-90% of modern software constitute OSS code. Yet we are stuck with tools that scan only for vulnerabilities in 3rd party libraries and that too with high degree of false positives. I built `vet` for policy and data driven analysis of 3rd party packages that goes beyond only vulnerability and allows codifying organisational policies related to OSS consumption. https://github.com/safedep/vet Looking forward to feedback and suggestions from HN :)
2023 · github.com · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →