Dev tools · alternatives · 2026

24 alternatives to GitGuardian Shield
Open sourced application to detect security vulnerabilities.
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes. GitGuardian Shield launched in 2020; newer entries below may have overtaken it.
- 1
 GitGuardian▲132
Detect secrets in source code, public and private!
2018 · gitguardian.com · its alternatives →
- 2

- 3

- 4
 GitHits beta 0.9▲181
It has been almost 10 years since I started the opencv-python packaging project. Scaling it to more than 100 million downloads as a side project showed me how much ease of installation and proper package distribution matter to users. It gave the computer vision ecosystem a noticeable boost. Now I have a new idea that I hope can help even more people across the broader software engineering world. A while ago, I realized I kept giving the same advice to teammates and friends when they ran into a programming issue they couldn't easily solve: go to GitHub and look at how others solved it. There…
Jun 2026 · githits.com · its alternatives →
- 5

I noticed the growing security concerns around MCP (https://news.ycombinator.com/item?id=43600192) and built an open source tool that can detect several patterns of tool poisoning attacks, exfiltration channels and cross-origin manipulations. MCP-Shield scans your installed servers (Cursor, Claude Desktop, etc.) and shows what each tool is trying to do at the instruction level, beyond just the API surface. It catches hidden instructions that try to read sensitive files, shadow other tools' behavior, or exfiltrate data. Example of what it detects: - Hidden instructions…
2025 · github.com · its alternatives →
- 6
 Bearer CLI▲174
Free & open source security scanner for developers
2023 · cycode.com · its alternatives →
- 7GM
2017 · gitmonkey.io · its alternatives →
- 8
Protecting free expression from digital attacks
2022 · projectshield.withgoogle.com · its alternatives →
- 9

Hi! I got tired of setting up tools I can't explain to a team in a few words like sops or git-crypt, just to store few files with environment variables or secrets, so I built lockenv as a simple alternative. It's basically a password-protected vault file you commit to git. No gpg keys, no cloud, just lockenv init, set a password, and lock/unlock the secrets. This tool integrates with OS keyring, so you're not typing passwords constantly. Should work on Mac/Linux/Windows, but I tested it only on linux so far. I am not trying to replace any mature / robust solution, just…
Dec 2025 · github.com · its alternatives →
- 10BO
Hi HN, we’re the co-founders of Bearer, and today we launch an open-source alternative to code security solutions such as Snyk Code, SonarQube, or Checkmarx. Essentially, we help security & engineering teams to discover, filter and prioritize security risks and vulnerabilities in their codebase, with a unique approach through sensitive data (PII, PD, PHI). Our website is at https://www.bearer.com and our GitHub is here: https://github.com/bearer/bearer We are not originally Security experts but have been software developers and engineering leaders for over 15…
2023 · its alternatives →
- 11
 Shieldstral▲104
Define safety at runtime for text and images
Aug 2026 · mistral.ai · its alternatives →
- 12

Finally open sourced an internal tool we've been using for managing secrets. It's similar to SOPS, but more opinionated, easier to configure/use correctly, and produces nicer git diffs. It also supports one-way encryption, so you don't have to know the private key to add secrets.
2023 · github.com · its alternatives →
- 13
 SafeDep Vet▲72
GitLab CI Component that lets you seamlessly protect your pipelines from vulnerable and malicious open source dependencies. The component integrates directly into your CI/CD workflow through the GitLab CI Catalog and allows you to establish policy-driven guardrails using Common Expression Language (CEL). Key features: - Set your own opinionated security policies as code using CEL - Detect and block risky OSS components before they enter your codebase - Seamless integration as a native GitLab CI Component - Available directly in the GitLab CI Catalog Try and lets us know our thoughts!
2023 · safedep.io · its alternatives →
- 14

Automated security assistant for developers
2020 · shieldfy.io · its alternatives →
- 15

aToday, we’re excited to announce that we’re going to be able to build tools that impact almost every software developer on the planet — we’re joining GitHub.
2015 · appcanary.com · its alternatives →
- 16GC
I authenticate to many Git hosts from many machines and got tired of generating and copying personal access tokens. With credential helper git-credential-oauth, there are no personal access tokens or SSH keys to configure. Instead you authenticate in browser using OAuth. Git Credential Manager (included with Git for Windows) has a similar feature but it's awkward for Linux users to install. git-credential-oauth is cross platform and packaged in many Linux distributions.
2023 · its alternatives →
- 17
- 18

2014 · github.com · its alternatives →
- 19

Find & fix open source vulnerabilities - for all languages
2018 · github.com · its alternatives →
- 20
I got fed up with endless PR reviews and the constant fear of missing a security bug, so I built Shieldcode. What it does: - Scans new pull requests for bugs and vulnerabilities automatically - Comments directly on GitHub with clear, actionable feedback - Works out of the box with no complex setup required Next up: NPM VScan, which will check your npm dependencies on every push for vulnerabilities or malware. I’d love to hear your thoughts and feedback! https://shieldcode.space
2025 · shieldcode.space · its alternatives →
- 21

Zero-Trust access management with true WireGuard® 2FA/MFA - DefGuard/defguard
2023 · github.com · its alternatives →
- 22OS
2024 · defguard.net · its alternatives →
- 23GP
Hey HN, Every team I've been on has cobbled together some sort of combination of GitHub branch protections and custom scripts to make sure that PRs conform to organization policies and best practices. Things like: - When {X} file is changed, require review from team {Y} - When a new db migration is added, ensure that a special set of tests pass - Require multiple approvals when the PR is very large - Add a special label to PRs that include breaking changes - Allow emergencies / hotfixes to break glass and bypass all of the above Most teams tend to start out with a little script running…
2025 · gitguard.dev · its alternatives →
- 24
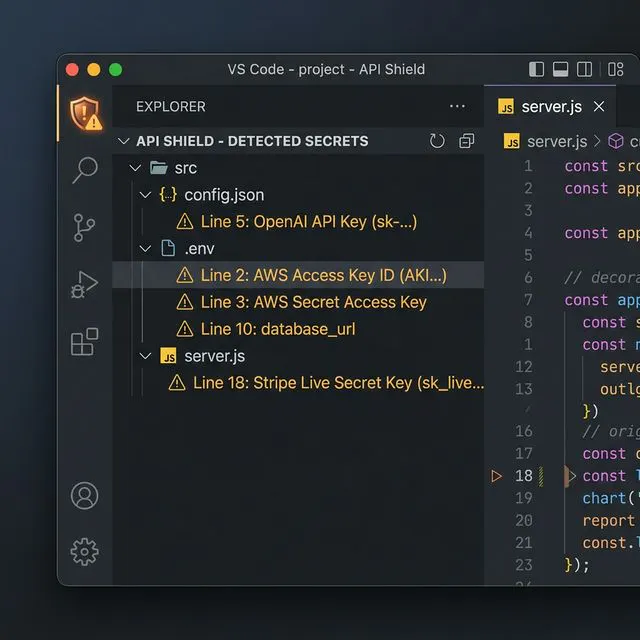
API Key & Secret Leak Detector
Mar 2026 · marketplace.visualstudio.com · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →