Dev tools · alternatives · 2026
24 alternatives to Qualysec Cloud Suite
Cloud security assessment for misconfigs and IAM risks
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

Vulnerability dashboard
2025 · dashboard.qualysec.com · its alternatives →
- 2
 KloudMate▲279
Logs, metrics, and traces in one platform. KloudMate helps engineers find and fix issues fast. Ask the built-in AI assistant to help track down the cause.
2023 · kloudmate.com · its alternatives →
- 3

Next-gen real-time CSPM to Identify, prioritize & remediate critical cloud security risks across AWS, Azure, Google cloud & Oracle cloud
2015 · cloudsploit.com · its alternatives →
- 4

Dear HN community! Looking forward to hearing your feedback on ACE (assured confidential execution), technology that implements VM-based trusted execution environment (TEE) for embedded RISC-V systems with focus on a formally verified and auditable firmware. We target high-assurance systems that can benefit from compartmentalization and hardware-backed isolation. The key ingredient called security monitor (firmware) is implemented in Rust. The formal specification is defined as annotations directly in code and gets translated to Coq using RefinedRust automation. ACE design is now part of the…
2025 · github.com · its alternatives →
- 5
 JetBrains Qodana▲154
Evaluate the integrity of code you own, contract or purchase
2021 · jetbrains.com · its alternatives →
- 6

- 7

- 8

Cloud spend visibility tool Finally Get Clarity On Cloud Spend Without Hours Lost In Dashboards
2018 · cloudforecast.io · its alternatives →
- 9

Move your SVN into the cloud
2017 · get.assembla.com · its alternatives →
- 10

- 11
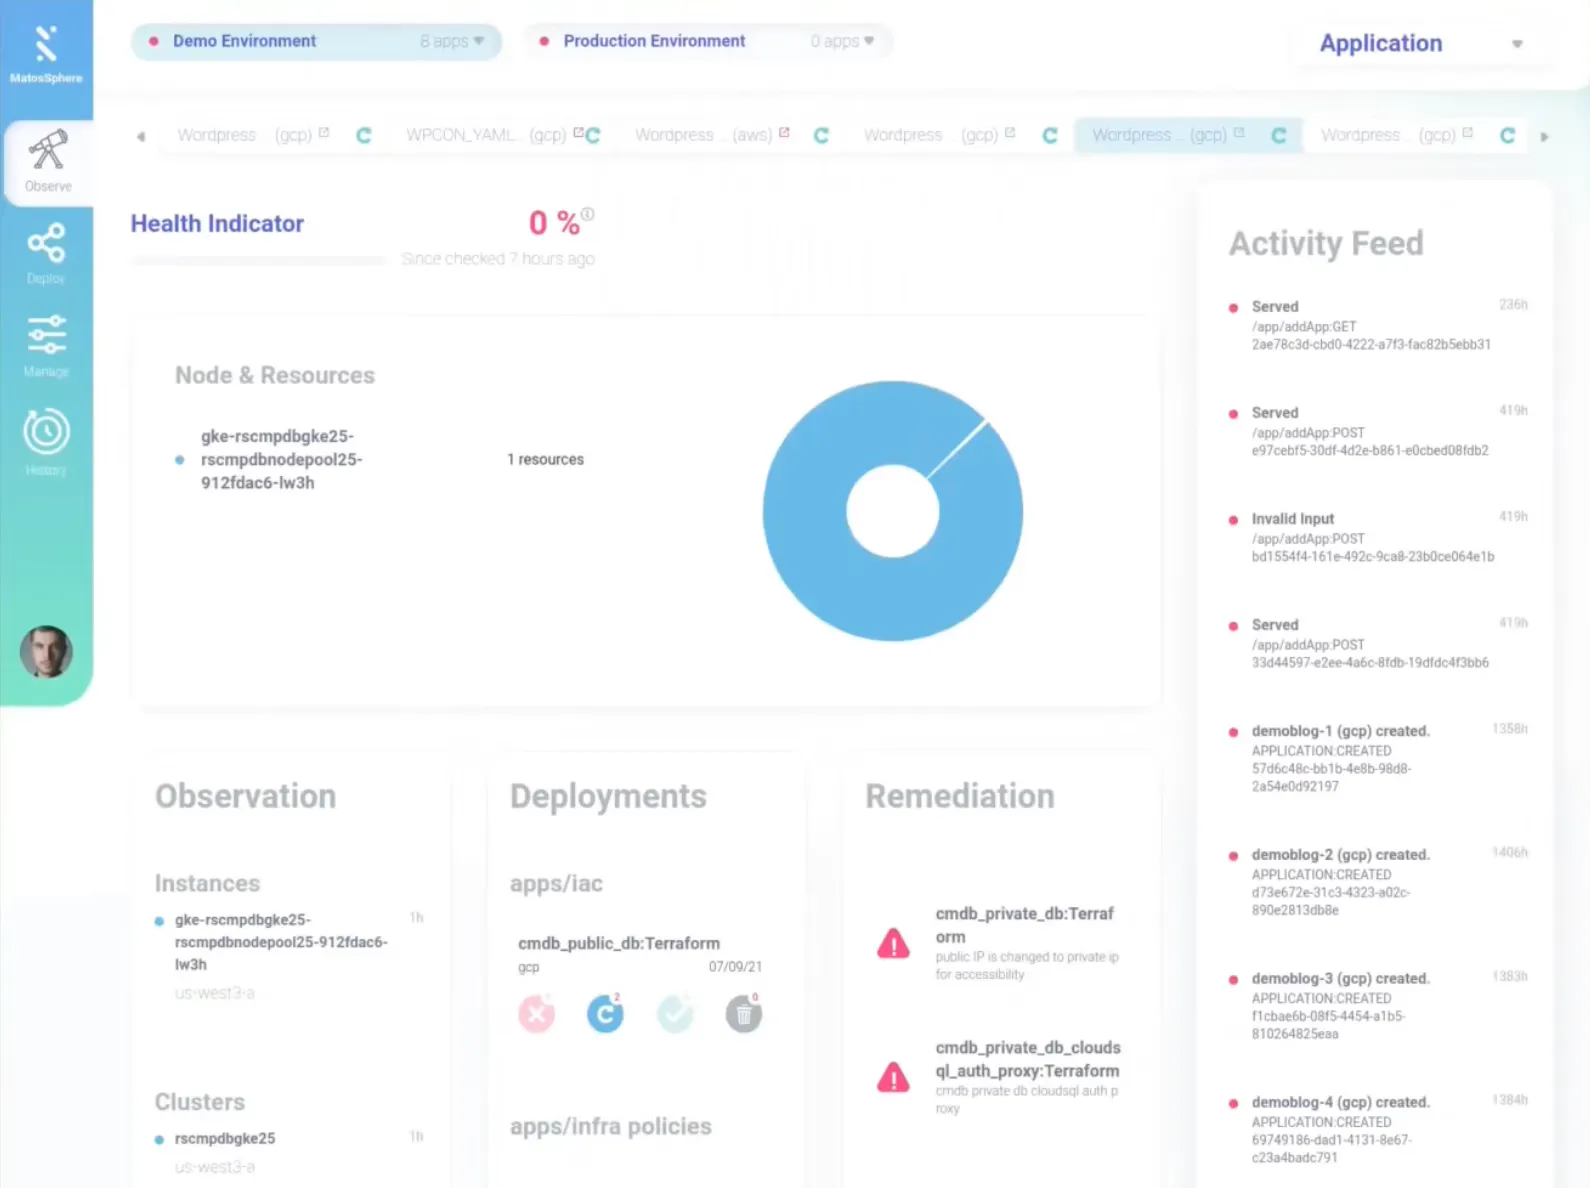 MatosSphere▲39
Observability Remediation to IT, DevOps, Cloud Engineering
2021 · cloudmatos.com · its alternatives →
- 12QI
Sunwin có uy tín không? Link truy cập mới nhất, cách tải app, đăng ký và kinh nghiệm chơi thực tế từ người trong cuộc. Đọc xong biết đủ để quyết định.
2018 · qeys.io · its alternatives →
- 13

Hi HN! I’m Arash, one of the founders of Strada (https://www.getstrada.com), a cloud IDE for building automation workflows across your company’s SaaS apps. Strada handles integrations, triggers, infrastructure and observability while letting you write core workflow logic in Python (more languages soon). It's for teams that hit limitations with low-code tools while building with internal apps — eg. Zendesk, Jira, Salesforce, Slack. You can access our docs at (https://docs.getstrada.com). While working on our first product (a unified accounting API), we learned that as…
2024 · getstrada.com · its alternatives →
- 14
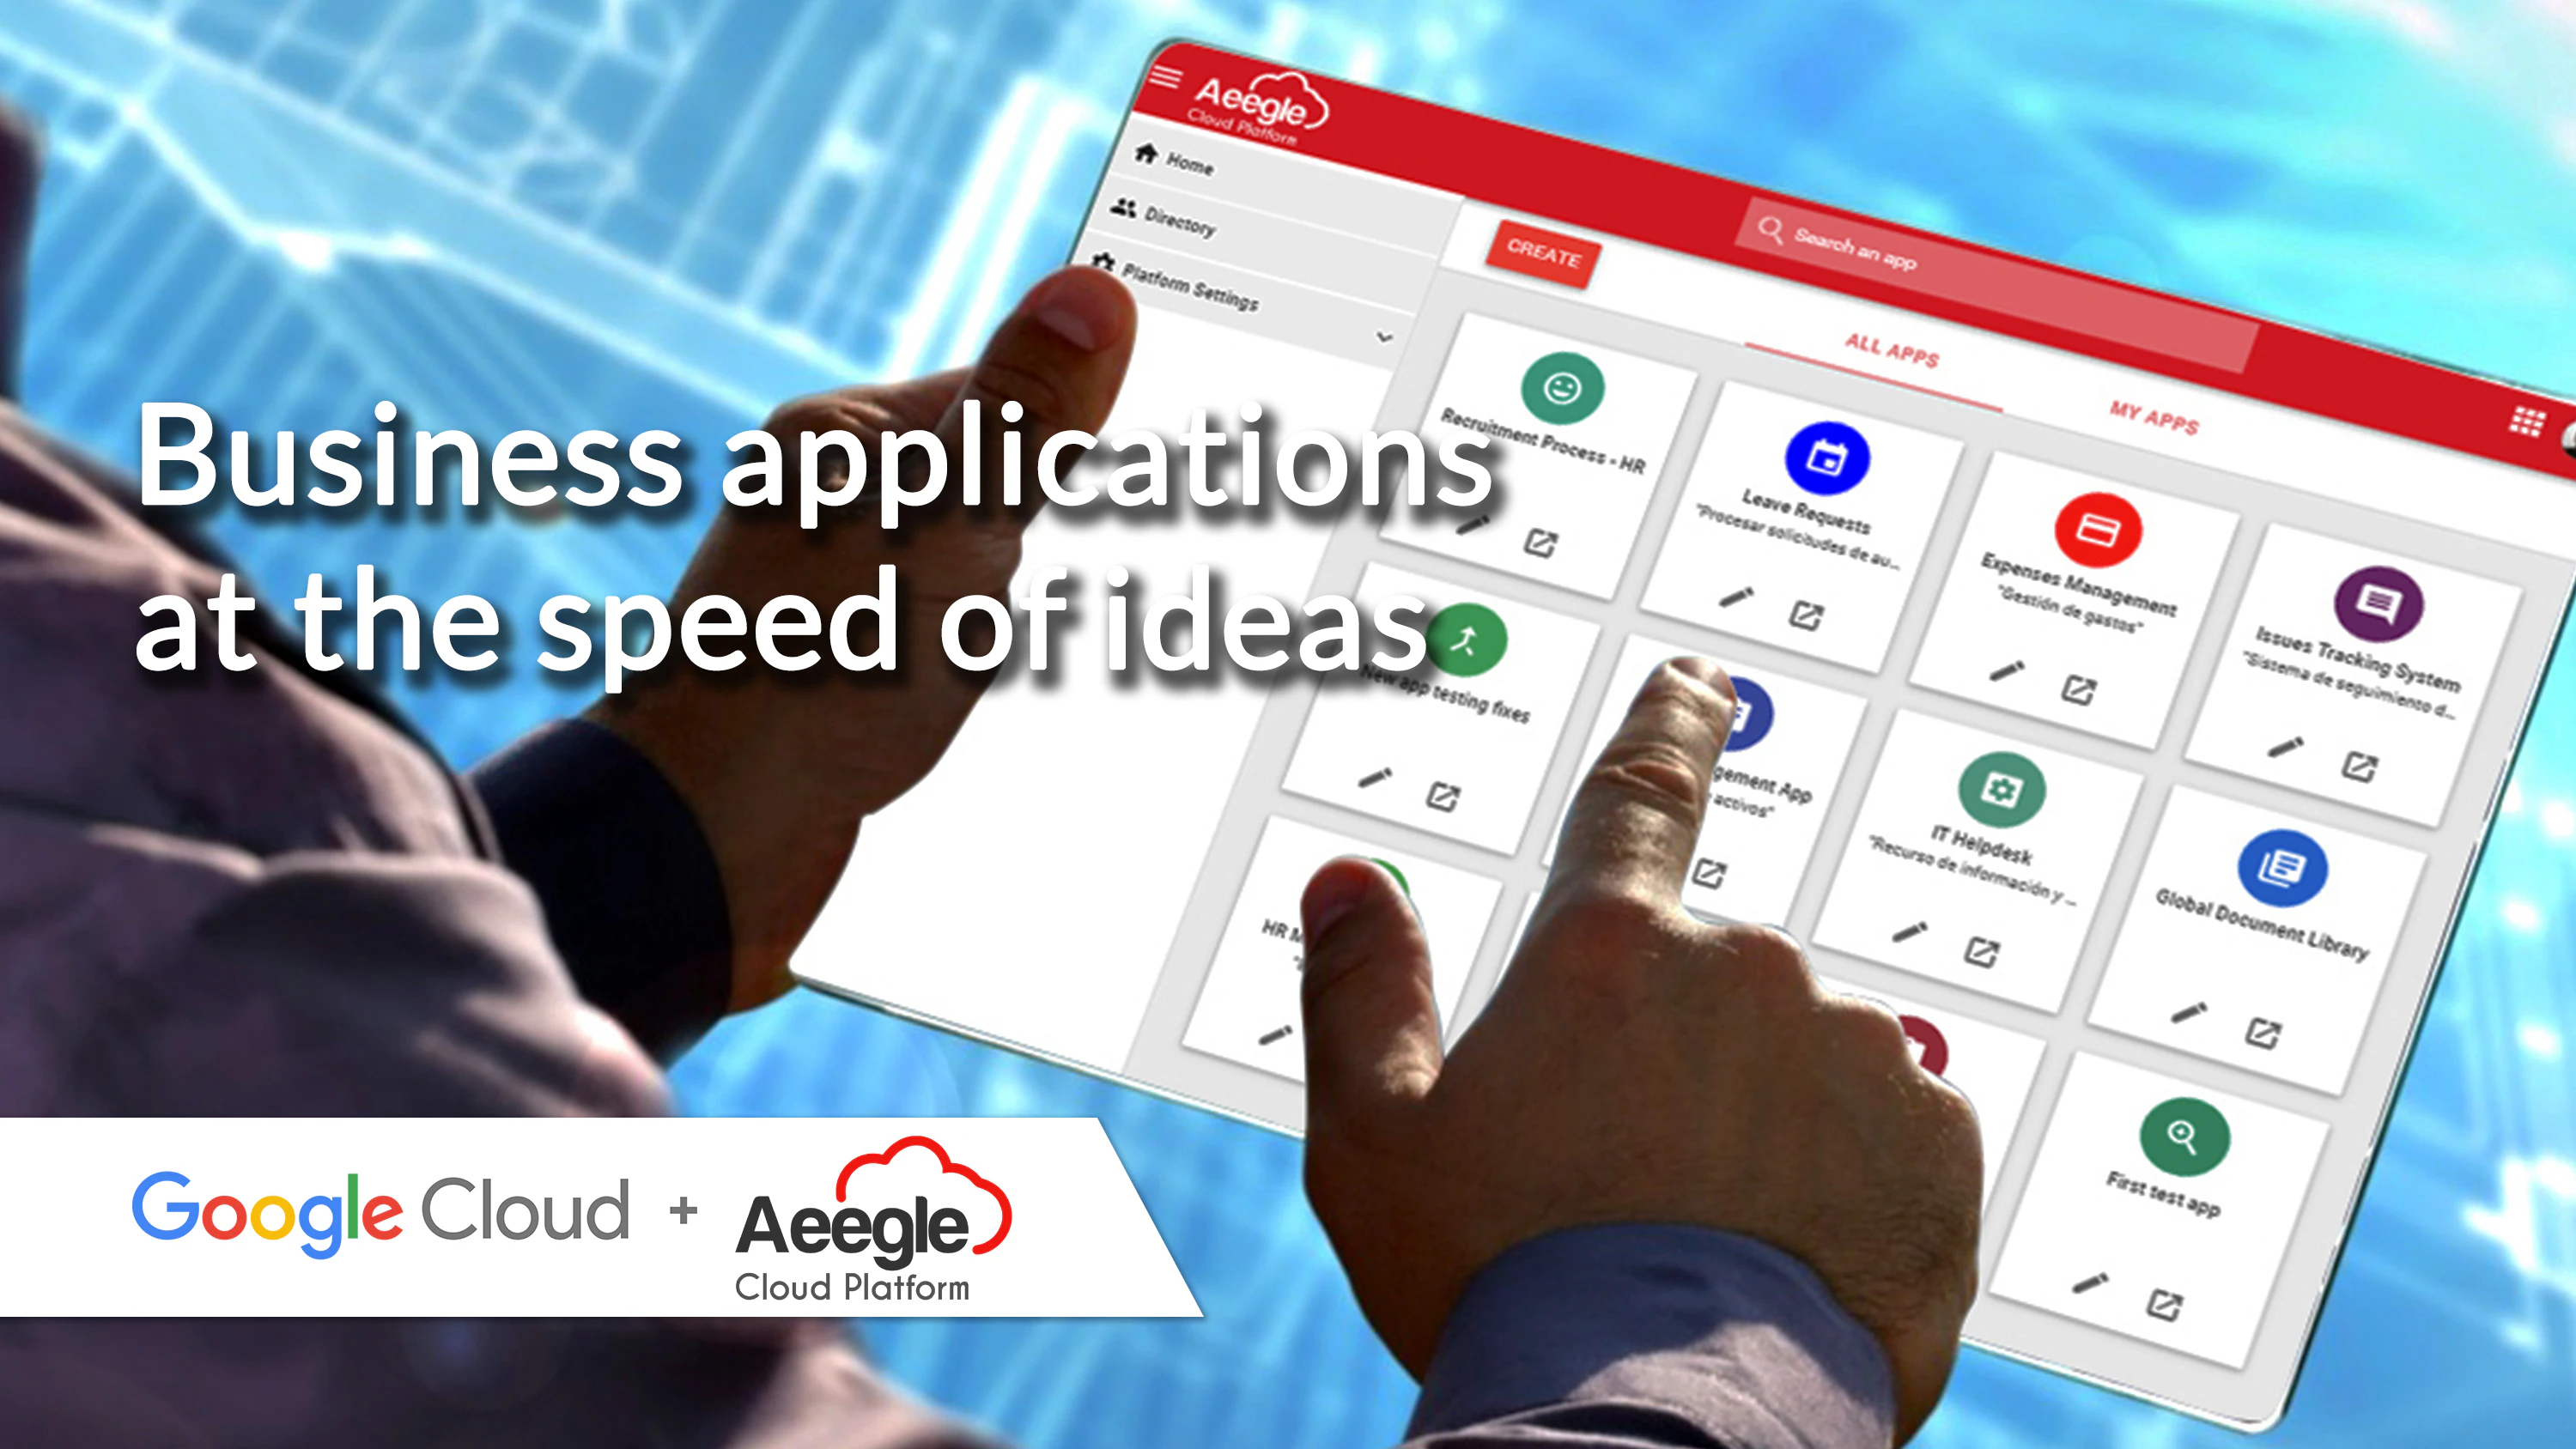
Enterprise-ready business applications builder for G-suite
2017 · cloud.aeegle.com · its alternatives →
- 15
- 16

Defend What Matters : Web Application Penetration Testing
2025 · qualysec.com · its alternatives →
- 17

Infrastructure as code (IaC) often fails during deployment due to dynamic constraints such as name collisions, quota limits and other resource-specific constraints that devs run halfway into an IaC deployment. We witnessed this first hand at TinyStacks and built precloud - an open-source framework to define and run dynamic tests before IaC deployments. The precloud framework currently supports Terraform and AWS CDK with several default checks (unique names, service quota checks and more) and ability to define your own!
2023 · github.com · its alternatives →
- 18

All-in-one devops solutions - cloudlaunchpad
2025 · cloudlaunchpad.app · its alternatives →
- 19

Manage AWS, GCP, Azure, Kubernetes, and 45+ cloud providers from one unified desktop and web app. SSH terminals, SQL editor, K8s exec, storage browser, and more.
Jul 2026 · infrawrench.com · its alternatives →
- 20FA
Hi, we’re Lukas, Lars and Matthias, and we're building “Fix” (https://fix.security). Fix is an open source cloud asset inventory for developers to track their infrastructure’s security posture aka “cloud security posture management” (CSPM). How Fix works: Fix takes a snapshot of your inventory on an hourly basis by calling the cloud APIs, runs policy and compliance checks such as the CIS benchmark against that inventory, and provides the findings in a dashboard, via .csv export or API so that developers can use the raw data and build workflows. We’re also working on data sync to S3…
2024 · fix.security · its alternatives →
- 21

Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report. - salesforce/cloudsplaining
2020 · github.com · its alternatives →
- 22
 TrailGuide▲18
Cloud security service with AWS insights & alerts
2024 · oslabs-beta.github.io · its alternatives →
- 23HO
Hello HN, I’m excited to share something we’ve been working on: Cloud Troubleshooting Labs. This tool provides on-demand environments for engineers to practice hands-on troubleshooting with AWS, GCP, Azure, and Kubernetes. What it does: We use Pulumi to spin up these environments. Each scenario includes a diagram and an explanation of the available IT infrastructure. Engineers are tasked with fixing configuration issues to make the application work. Depending on the test type, the environment could range from a simple terminal to a full cloud environment or a web-based VSCode. Many of our…
2024 · brokee.io · its alternatives →
- 24ZY
Hey folks - last month, we open sourced ZeusCloud (https://github.com/Zeus-Labs/ZeusCloud) - a platform to identify, prioritize, and remediate security risks in your cloud environment. ZeusCloud thinks like an attacker. It identifies security risks in your environment like infra misconfigurations, over-permissive identities, and workload vulnerabilities. And it pieces them together to show you attack paths like a publicly exposed VM with a critical CVE has effective admin access. Some highlights of the ZeusCloud platform: - Graphical attack paths so you can prioritize the…
2023 · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →