Dev tools · alternatives · 2026

24 alternatives to ScanReq
Find outdated deps and CVEs across 8 ecosystems in VS Code
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

An open source security scanner for Visual Studio Code
2020 · snyk.io · its alternatives →
- 2

Search millions of open source repos without leaving the IDE
2022 · marketplace.visualstudio.com · its alternatives →
- 3

Online automated vulnerability scanner to secure firewalls, servers, web applications, and apis. Try 14 days for free.
2020 · hostedscan.com · its alternatives →
- 4

- 5

This is a simple single-file python program that can find basic XSS (cross-site scripting) vulnerabilities in a target url. Most XSS discovery tools use a payload refelection strategy in which payloads are injected in url parameters and the GET response is inspected for places where the payload content is reflected. This is a very low precision XSS detection strategy because most reflection does not support execution. This program uses a different approach, and instead opens the target url in a browser, tests alert(...) payloads directly in the browser context, and listens for an alert being…
2024 · github.com · its alternatives →
- 6
 EOL Dataset▲64
Find every EOL dependency in your stack. Free. In 5 minutes.
Apr 2026 · herodevs.com · its alternatives →
- 7

World's Largest Exploit Database
2023 · exploit.observer · its alternatives →
- 8

I wanted a safer alternative to RegExp for TypeScript that uses a linear-time engine, so I built Regolith. Why: Many CVEs happen because TypeScript libraries are vulnerable to Regular Expression Denial of Service attacks. I learned about this problem while doing undergraduate research and found that languages like Rust have built-in protection but languages like JavaScript, TypeScript, and Python do not. This library attempts to mitigate these vulnerabilities for TypeScript and JavaScript. How: Regolith uses Rust's Regex library under the hood to prevent ReDoS attacks. The Rust Regex library…
2025 · github.com · its alternatives →
- 9CF
2012 · webscanservice.com · its alternatives →
- 10

- 11
Free security scan that tells you exactly how to fix it
Jun 2026 · its alternatives →
- 12
 AttackerView▲13
Last week I wrote about building a scanner that writes its own exploits. A cron job runs Claude Code every night, it reads new CVEs, writes proof-of-concept checks, tests them against vulnerable and patched Docker instances, and opens PRs. I review and merge in the morning. That post was about how t
Feb 2026 · attackerview.com · its alternatives →
- 13
 VibeScan▲9
Beta tool that runs OWASP/Nuclei/ZAP checks fast and prioritizes fixes; would love test runs on your staging domains and blunt feedback.
2025 · vibescan.co.kr · its alternatives →
- 14

- 15
 DeepScan▲10
Detect bugs and quality issues in JavaScript and TypeScript.
2017 · deepscan.io · its alternatives →
- 16
 VulScan▲4
Python security scanner that eliminates false positives
Feb 2026 · vulscan.nexorium.io · its alternatives →
- 17

- 18
 PwnScan▲8
For at least a few years (since before COVID), in my circle everbody wants an AI tool that finds vulnerabilities in binaries. I have my reservations about such a tool because of my perception that AI is overhyped, so I decided to build one myself to see how useful it could be (or not). I was actually kinda surprised how well it worked for my collection of binaries with known CVEs. It definitely has false positives and negatives, as any static analysis tool would, but I think its actually somewhat usable. I dont think the results are super actionable, but interesting nonetheless. I still…
2025 · pwnscan.com · its alternatives →
- 19

A fast way to scan your server for outdated software and potential exploits. - PatrolServer/bashscanner
2015 · github.com · its alternatives →
- 20

Linux Foundation survey says 70-90% of modern software constitute OSS code. Yet we are stuck with tools that scan only for vulnerabilities in 3rd party libraries and that too with high degree of false positives. I built `vet` for policy and data driven analysis of 3rd party packages that goes beyond only vulnerability and allows codifying organisational policies related to OSS consumption. https://github.com/safedep/vet Looking forward to feedback and suggestions from HN :)
2023 · github.com · its alternatives →
- 21

I built a GitHub app that detects it in pull requests, notifies or blocks them. Alongside it, I published a Semgrep ruleset for any stage of the CI/CD. I started this after getting frustrated by all the FUD around malicious code - lots of noise, little effort to solve it. Having said that, it's still a major attack vector - a stored RCE, with the codebase itself as the sink. Feedback is appreciated. The app, PRevent - https://github.com/apiiro/PRevent The ruleset: https://github.com/apiiro/malicious-code-ruleset The research:…
2025 · github.com · its alternatives →
- 22
 Vulert▲10
Open source monitoring: zero trust, no code access required
2024 · vulert.com · its alternatives →
- 23

- 24
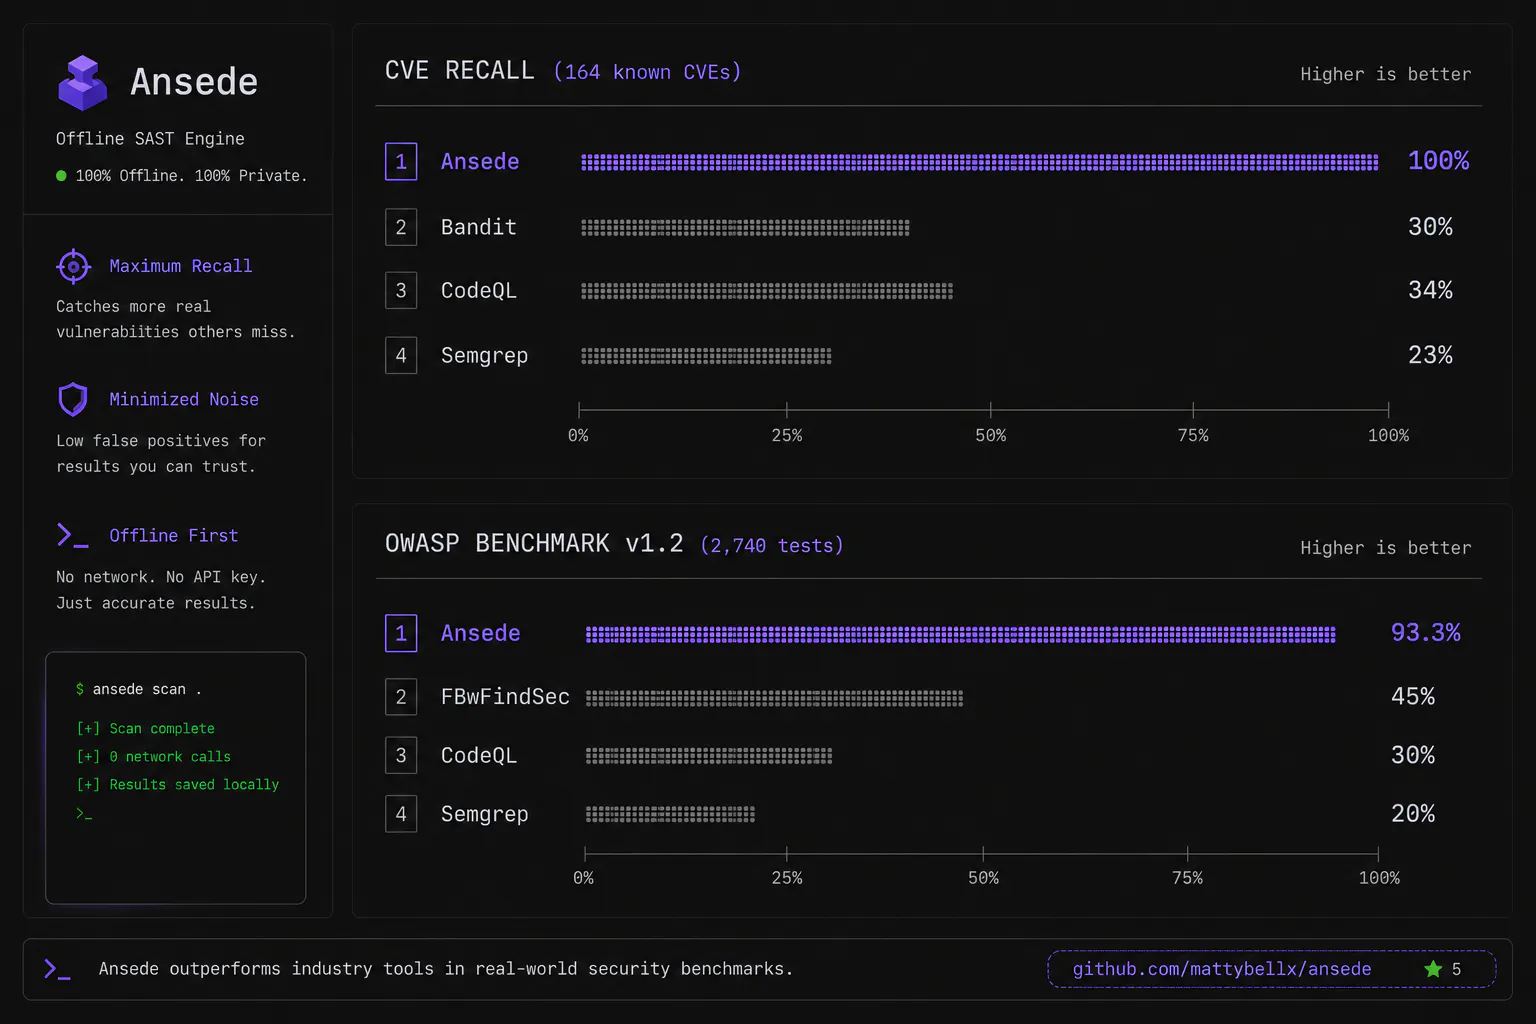
100% Offline SAST, Finds What Semgrep & CodeQL Miss
Jul 2026 · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →