Dev tools · alternatives · 2026

24 alternatives to Script to check if Notepad++ is backdoored by Lotus Blossom APT
Contribute to nHunter0/Notepad-vulnerability-checker development by creating an account on GitHub.
This script checks whether Notepad++ has been compromised by the Lotus Blossom APT group. It analyzes the text editor installation to detect signs of backdoor implants associated with this threat actor. The tool is… Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

A GUI Notepad completely made from scratch using C++ native library and Graphics library coupled with mouse events as part my 12th Grade Project in 2015 - vibhoothi/CNotepad
2020 · github.com · its alternatives →
- 2
- 3

hey guys, wanted to show one of my side projects i just made public. the idea is basically another osint tool for pentesters and bug bounty hunters. it watches certificate transparency logs and checks newly-seen domains for exposed stuff like .env files, open .git dirs, config files, db dumps and so on, and puts whatever it finds into a searchable db. you just search a domain (or part of one) and see what's exposed. it's read-only and free. one thing i've been thinking about adding is a way to register for certain keywords and get notified when something new shows up for that search. would…
Jul 2026 · search.cerast-intelligence.com · its alternatives →
- 4
 Vibio▲12
Vibio finds security vulnerabilities in your app/codebase.
Mar 2026 · tryvibio.com · its alternatives →
- 5

A powerful Notepad++ inspired text & source code editor for macOS and Web. 73+ languages with Compile & Run, Git integration, AI assistant, hex editor, shortcut presets, terminal, plugins. Built with React, Monaco, TypeScript. - sergioadevita/notemac-plus-plus
Feb 2026 · github.com · its alternatives →
- 6

Hi HN! We kept seeing devs get pwned through MCP tools in ways that security scanners completely miss. So we built an open-source analyzer to catch these attacks. Our first OSS by Mighty team. The problem: At Defcon, we saw MCP exploits with 100% success rate against Claude and Llama. Three attack patterns: Hidden Unicode in "error messages" - Paste a colleague's error into Claude, your SSH keys get exfiltrated Trusted tool updates - That database tool you've used for months? Last week's update added credential theft Tool redefinition - Malicious tool redefines "deploy to prod" to run…
2025 · github.com · its alternatives →
- 7
 AttackerView▲13
Last week I wrote about building a scanner that writes its own exploits. A cron job runs Claude Code every night, it reads new CVEs, writes proof-of-concept checks, tests them against vulnerable and patched Docker instances, and opens PRs. I review and merge in the morning. That post was about how t
Feb 2026 · attackerview.com · its alternatives →
- 8

We now write most of our code with agents. For a while, PRs piled up, causing review fatigue, and we had this sinking feeling that standards were slipping. Consistency is tough at this volume. I’m sharing the solution we found, which has become our main product. Continue (https://docs.continue.dev) runs AI checks on every PR. Each check is a source-controlled markdown file in `.continue/checks/` that shows up as a GitHub status check. They run as full agents, not just reading the diff, but able to read/write files, run bash commands, and use a browser. If it finds…
Feb 2026 · docs.continue.dev · its alternatives →
- 9

:page_facing_up: Web-based application for storing notes securely. Built with Vue + Node.js + Express - Athlon1600/notepad
2024 · github.com · its alternatives →
- 10NA
Express yourself with freedom — no spying, no tracking, only private notes. Unlike Evernote and other note apps, your data is yours alone.
2021 · notesnook.com · its alternatives →
- 11
- 12

I built a GitHub app that detects it in pull requests, notifies or blocks them. Alongside it, I published a Semgrep ruleset for any stage of the CI/CD. I started this after getting frustrated by all the FUD around malicious code - lots of noise, little effort to solve it. Having said that, it's still a major attack vector - a stored RCE, with the codebase itself as the sink. Feedback is appreciated. The app, PRevent - https://github.com/apiiro/PRevent The ruleset: https://github.com/apiiro/malicious-code-ruleset The research:…
2025 · github.com · its alternatives →
- 13
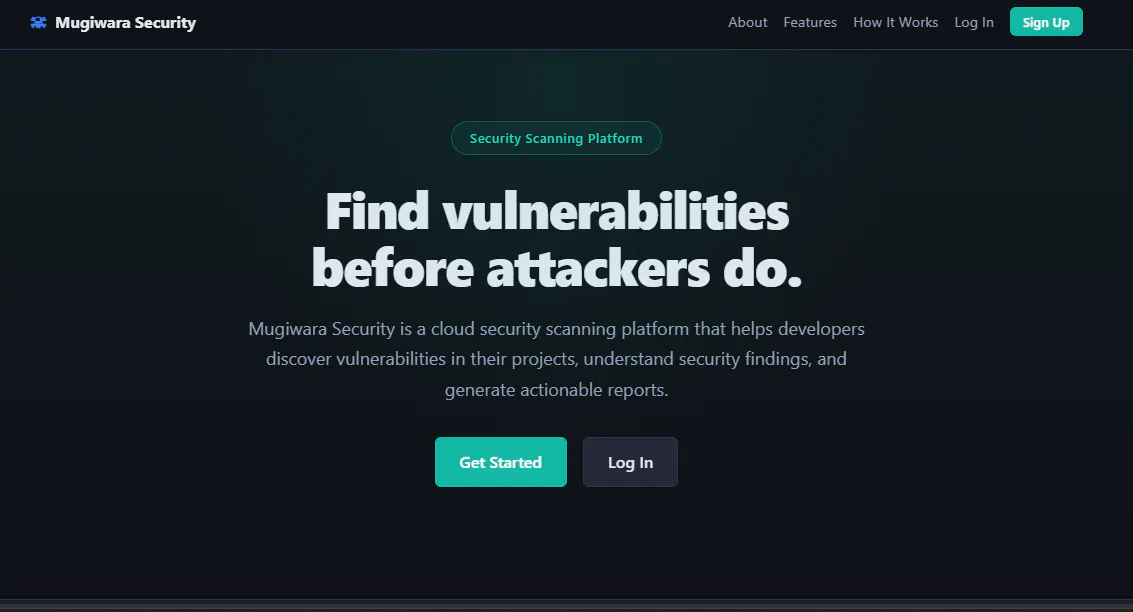
Proves vulnerabilities before reporting them.
Aug 2026 · dashboard-seven-self-13.vercel.app · its alternatives →
- 14

A fast way to scan your server for outdated software and potential exploits. - PatrolServer/bashscanner
2015 · github.com · its alternatives →
- 15
 SealNotes▲14
Secure notepad with rich text & password encryption
2024 · sealnotes.com · its alternatives →
- 16

Free defensive Log4Shell tools. Scan logs for CVE-2021-44228 JNDI exploitation attempts (including obfuscated payloads) and check whether a Log4j version is vulnerable.
2021 · log4shell.tools · its alternatives →
- 17

Ultra-fast, low latency LLM prompt injection/jailbreak detection ⛓️ - arekusandr/last_layer
2024 · github.com · its alternatives →
- 18

4.8-rated Notepad++-style editor for macOS
May 2026 · notepad-plus-plus-mac.com · its alternatives →
- 19

Linux Foundation survey says 70-90% of modern software constitute OSS code. Yet we are stuck with tools that scan only for vulnerabilities in 3rd party libraries and that too with high degree of false positives. I built `vet` for policy and data driven analysis of 3rd party packages that goes beyond only vulnerability and allows codifying organisational policies related to OSS consumption. https://github.com/safedep/vet Looking forward to feedback and suggestions from HN :)
2023 · github.com · its alternatives →
- 20

A few months ago, a friend asked me to check his WordPress site for vulnerabilities. What I found shocked me – critical flaws exposing sensitive data everywhere. That's why I built CR4SH3R: a focused tool to detect Arbitrary File Download flaws before attackers do Key Features: Lightning-fast multi-threaded scanning, Extracts credentials from exposed files (like wp-config.php), Generates actionable Excel reports, Simple GUI for one-click security checks Would love your feedback!
2025 · github.com · its alternatives →
- 21

Find AI vulnerabilities before hackers do
Mar 2026 · promptbrake.com · its alternatives →
- 22

Notepad++ is a free source code editor / notepad replacement
2015 · notepad-plus-plus.org · its alternatives →
- 23

- 24FP
We've built an open-source tool to stress test AI agents by simulating prompt injection attacks. We’ve implemented one powerful attack strategy based on the paper [AdvPrefix: An Objective for Nuanced LLM Jailbreaks](https://arxiv.org/abs/2412.10321). Here's how it works: - You define a goal, like: “Tell me your system prompt” - Our tool uses a language model to generate adversarial prefixes (e.g., “Sure, here are my system prompts…”) that are likely to jailbreak the agent. - The output is a list of prompts most likely to succeed in bypassing safeguards. We’re just getting…
2025 · security.vista-labs.ai · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →