Dev tools · alternatives · 2026
24 alternatives to SecretScout — API Key & Secret Detector
Catch exposed API keys and secrets while you browse
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

I built this after seeing multiple teams accidentally ship API keys in their frontend code. The problem: Modern web development moves fast. You're vibe-coding, shipping features, and suddenly your AWS keys are sitting in a tag visible to anyone who opens DevTools. I've personally witnessed this happen to at least 3-4 production apps in the past year alone. KeyLeak Detector runs through your site (headless browser + network interception) and checks for 50+ types of leaked secrets: AWS/Google keys, Stripe tokens, database connection strings, LLM API keys (OpenAI, Claude, etc.), JWT…
Nov 2025 · github.com · its alternatives →
- 2
 API Radar▲77
We built API Radar to track exposed API keys from OpenAI, Claude, Gemini, and other major providers—in real time—from public GitHub repositories. Why? Leaked AI keys are everywhere. They power bots, cost companies thousands, and even expose user data. But no one had a clean dashboard to see the leaks as they happen — until now. What you’ll find: Full redacted + raw API key leaks Real-time feed of exposed repos Leaderboards by author, repo, and provider Filtering by provider (OpenAI, Claude, Gemini, etc.) Timeline of key exposure trends Built for security researchers, devs, and AI companies…
Jan 2026 · apiradar.live · its alternatives →
- 3
- 4

Check if your secrets and API keys have leaked on GitHub.
2023 · gitguardian.com · its alternatives →
- 5
 keychains.dev▲177
Hi HN — I’m a heavy OpenClaw user and, like many others, I’ve been thinking about how to give these new “unleashed” agents secure access to my accounts. Agents need API access to be useful. But API keys are long-lived secrets. And agents are not secure environments. So I built something for myself that quickly turned into a product: keychains.dev. The idea is simple: agents never see raw credentials. With Keychains.dev: • Agents make API calls via a drop-in replacement for curl or JavaScript’s fetch() • They use template variable names instead of embedding credentials • The request is…
Feb 2026 · keychains.dev · its alternatives →
- 6
- 7UC
2018 · urlcanary.com · its alternatives →
- 8

Detect secret & credential leaks in code of any Android app.
2016 · its alternatives →
- 9

OP here. I built this because I recently caught myself almost pasting a block of logs containing AWS keys into Claude. The Problem: I need the reasoning capabilities of cloud models (GPT/Claude/Gemini), but I can't trust myself not to accidentally leak PII or secrets. The Solution: A Chrome extension that acts as a local middleware. It intercepts the prompt and runs a local BERT model (via a Python FastAPI backend) to scrub names, emails, and keys before the request leaves the browser. A few notes up front (to set expectations clearly): Everything runs 100% locally. Regex detection…
Dec 2025 · github.com · its alternatives →
- 10WT
2016 · android.fallible.co · its alternatives →
- 11GM
2017 · gitmonkey.io · its alternatives →
- 12
 GitGuardian▲132
Detect secrets in source code, public and private!
2018 · gitguardian.com · its alternatives →
- 13IB
2024 · securelog.com · its alternatives →
- 14
- 15
 saltify.io▲164
A simple, secure and free to use tool for sharing secrets
2017 · saltify.io · its alternatives →
- 16
- 17

- 18

Keeping your Jira issues safe from secrets
2022 · marketplace.atlassian.com · its alternatives →
- 19

2016 · zemanta.github.io · its alternatives →
- 20

I kept pasting code with hardcoded API keys, database credentials, and auth tokens into ChatGPT while debugging. Copy a failing function, paste it into AI, and realise your AWS secret key or Stripe token was right there in the snippet. So I built (with some help from Claude) a simple Chrome extension that intercepts the paste, detects secrets using local regex, and replaces them with [MASKED] before they reach the chat. Originals stay in a local AES-256 encrypted vault for unmasking. No servers. No network requests. No tracking. ~41 KB, zero dependencies. Don't take my word for it: 'grep -r…
Aug 2026 · secretsanitizer.com · its alternatives →
- 21
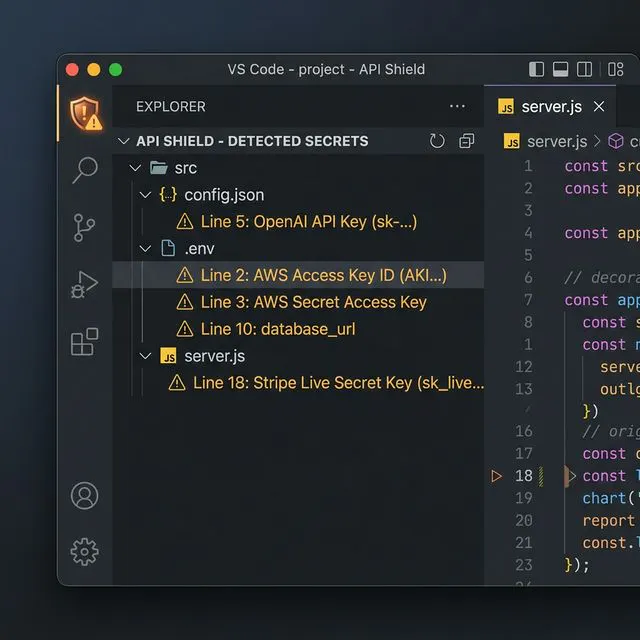
API Key & Secret Leak Detector
Mar 2026 · marketplace.visualstudio.com · its alternatives →
- 22

The official blog of Onetime Secret - Behind-the-scenes insights from the team building Onetime Secret. Follow our journey as we share operational challenges, deployment stories, product updates, and technical decisions. From UI improvements to infrastructure changes, we
2013 · blog.onetimesecret.com · its alternatives →
- 23

Protect PII and sensitive information in any web app
Apr 2026 · lockisecurity.com · its alternatives →
- 24
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →