Dev tools · alternatives · 2026
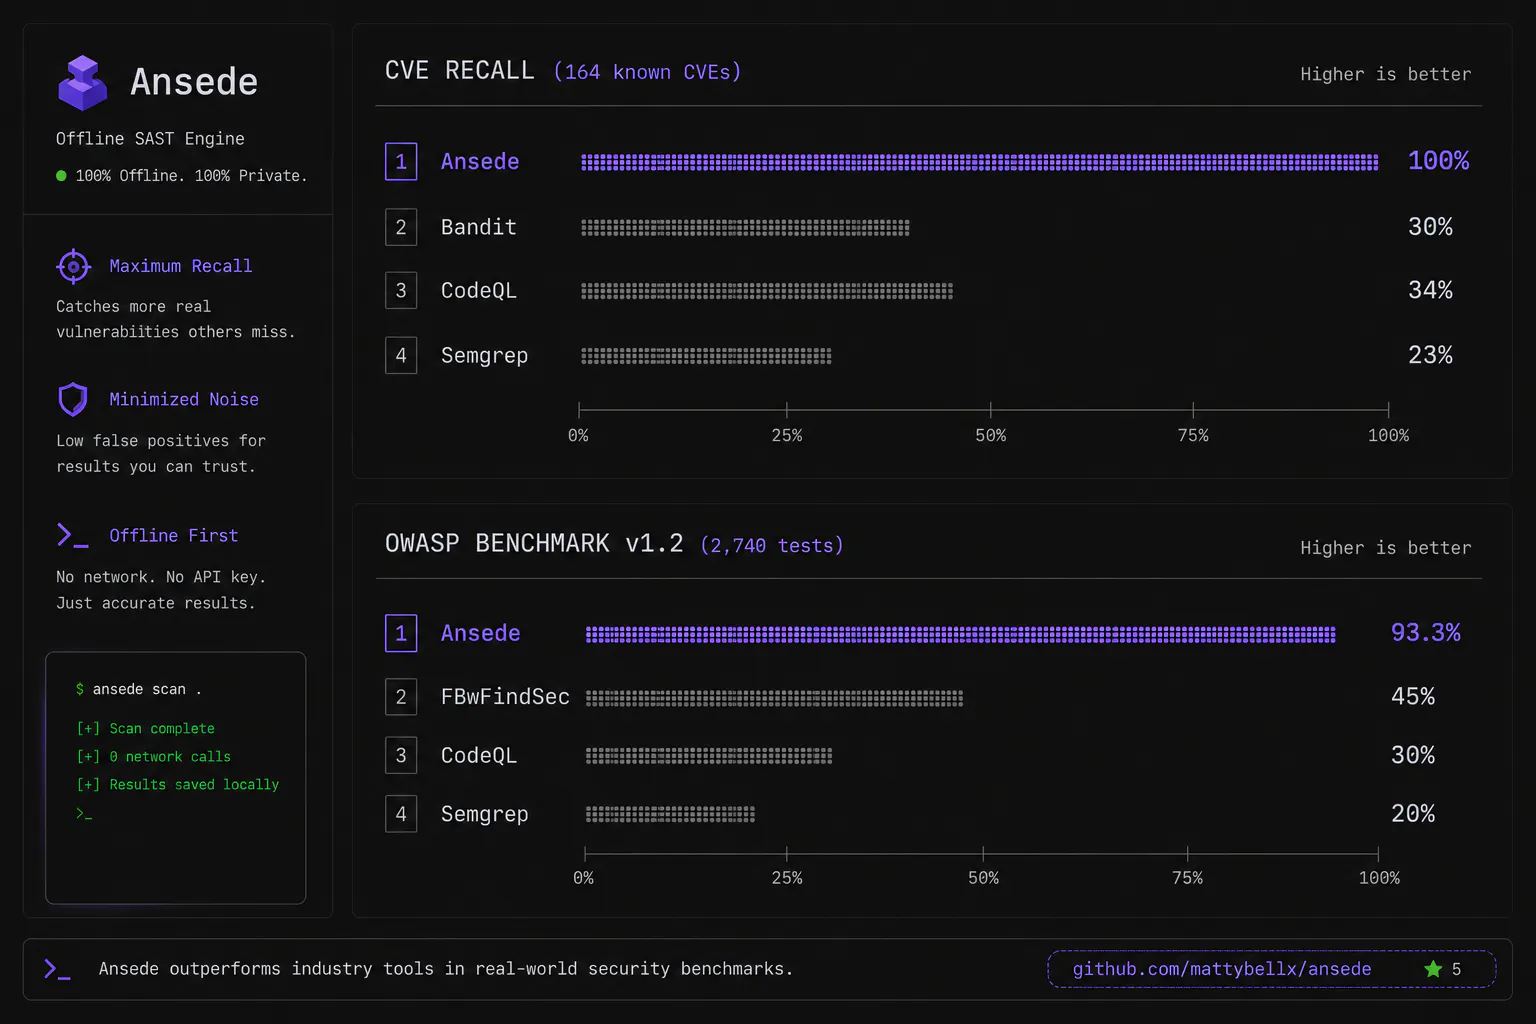
24 alternatives to Ansede. Live Security Scanner Playground
100% Offline SAST, Finds What Semgrep & CodeQL Miss
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

Secure code in less than 5 minutes for free
2022 · contrastsecurity.com · its alternatives →
- 2
 CodeThreat▲104
AI that spots real risks and keeps your code safe.
2023 · codethreat.com · its alternatives →
- 3
 CYREX▲62
Web security vulnerability assessment & penetration testing
2021 · cyrex.tech · its alternatives →
- 4

- 5EY
2019 · secalerts.co · its alternatives →
- 6
 AttackerView▲13
Last week I wrote about building a scanner that writes its own exploits. A cron job runs Claude Code every night, it reads new CVEs, writes proof-of-concept checks, tests them against vulnerable and patched Docker instances, and opens PRs. I review and merge in the morning. That post was about how t
Feb 2026 · attackerview.com · its alternatives →
- 7

World's Largest Exploit Database
2023 · exploit.observer · its alternatives →
- 8
 Probely▲87
Intuitive and easy-to-use webapp vulnerability scanner
2018 · probely.com · its alternatives →
- 9SASemgrep App▲79
https://semgrep.dev/products/semgrep-app Hi! I work on Semgrep, an open-source project (discussed on HN previously [0][1)]. We’re one of those companies that maintain an OSS tool and a web app, and then monetize by selling enterprise features on said web app. Our free web app just went through a major revamp (sort of like a v1.0 release) so this feels like the perfect time to share and hear what the HN crowd thinks! Let me start with some backstory on Semgrep. Our team, r2c, has been experimenting with various ways to help organizations step up their application security…
2021 · its alternatives →
- 10

Observer — scan your code for security issues, 100% offline
Aug 2026 · github.com · its alternatives →
- 11

I built a GitHub app that detects it in pull requests, notifies or blocks them. Alongside it, I published a Semgrep ruleset for any stage of the CI/CD. I started this after getting frustrated by all the FUD around malicious code - lots of noise, little effort to solve it. Having said that, it's still a major attack vector - a stored RCE, with the codebase itself as the sink. Feedback is appreciated. The app, PRevent - https://github.com/apiiro/PRevent The ruleset: https://github.com/apiiro/malicious-code-ruleset The research:…
2025 · github.com · its alternatives →
- 12TS
Hi HN, I’m Guillaume, the cofounder of Bearer, an Open Source SAST solution. After launching a few weeks ago here on Hacker News with support for Ruby and JavaScript stacks, I’m happy to report we’ve just released a new version (v1.2) with TypeScript support! In terms of code coverage, we use the same rules already implemented for vanilla JavaScript, but as usual, you can build your own. The rules list is here: https://docs.bearer.com/reference/rules/ It’s a first version for TS, but we believe that thanks to the pre-existing JavaScript support it should already…
2023 · its alternatives →
- 13

Online automated vulnerability scanner to secure firewalls, servers, web applications, and apis. Try 14 days for free.
2020 · hostedscan.com · its alternatives →
- 14

This is a simple single-file python program that can find basic XSS (cross-site scripting) vulnerabilities in a target url. Most XSS discovery tools use a payload refelection strategy in which payloads are injected in url parameters and the GET response is inspected for places where the payload content is reflected. This is a very low precision XSS detection strategy because most reflection does not support execution. This program uses a different approach, and instead opens the target url in a browser, tests alert(...) payloads directly in the browser context, and listens for an alert being…
2024 · github.com · its alternatives →
- 15
 ScanReq▲4
Find outdated deps and CVEs across 8 ecosystems in VS Code
Jun 2026 · scanreq.com · its alternatives →
- 16

Analyze your website's security with VULNWatch
2025 · vulnwatch.tech · its alternatives →
- 17

- 18

Modern Python source code security analyzer.
Jul 2026 · nocomplexity.com · its alternatives →
- 19CF
2012 · webscanservice.com · its alternatives →
- 20

We're open-sourcing Sighthound today, our rules-based static security scanner. What makes it special is that it's coded in rust and uses tree-sitter as it's AST making it very fast and easily extensible. Why build another scanner in 2026? We wanted to improve some of our detection outcomes but noticed the current open source scanners like Semgrep/Opengrep we're capped by a bunch of adoption limitations such as being written in OCaml, requiring a lot of work to add a language parser, and the rulesets were licensed differently and required paid offerings. It also felt that licensing was…
Jul 2026 · github.com · its alternatives →
- 21
Free security scan that tells you exactly how to fix it
Jun 2026 · its alternatives →
- 22

- 23

Scan any website for security flaws in one click
Nov 2025 · chromewebstore.google.com · its alternatives →
- 24

Passive blue-team security scanner — 582 read-only modules, plus 32 opt-in probes. Runs on your machine. No accounts. No telemetry. - taylannuhogluofficial-png/Tblue
Aug 2026 · github.com · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →