AI · alternatives · 2026

24 alternatives to CyberGuard
60% of startups leak API keys on GitHub. Find & Auto fix.
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

Check if your secrets and API keys have leaked on GitHub.
2023 · gitguardian.com · its alternatives →
- 2
 GitGuardian▲132
Detect secrets in source code, public and private!
2018 · gitguardian.com · its alternatives →
- 3
 API Radar▲77
We built API Radar to track exposed API keys from OpenAI, Claude, Gemini, and other major providers—in real time—from public GitHub repositories. Why? Leaked AI keys are everywhere. They power bots, cost companies thousands, and even expose user data. But no one had a clean dashboard to see the leaks as they happen — until now. What you’ll find: Full redacted + raw API key leaks Real-time feed of exposed repos Leaderboards by author, repo, and provider Filtering by provider (OpenAI, Claude, Gemini, etc.) Timeline of key exposure trends Built for security researchers, devs, and AI companies…
Jan 2026 · apiradar.live · its alternatives →
- 4

I built this after seeing multiple teams accidentally ship API keys in their frontend code. The problem: Modern web development moves fast. You're vibe-coding, shipping features, and suddenly your AWS keys are sitting in a tag visible to anyone who opens DevTools. I've personally witnessed this happen to at least 3-4 production apps in the past year alone. KeyLeak Detector runs through your site (headless browser + network interception) and checks for 50+ types of leaked secrets: AWS/Google keys, Stripe tokens, database connection strings, LLM API keys (OpenAI, Claude, etc.), JWT…
Nov 2025 · github.com · its alternatives →
- 5
- 6E2
Hey HN, I'm so happy to finally show you all this release after years of hard work. I posted the first version of EnvKey to HN back in 2017 (https://news.ycombinator.com/item?id=15330757), then went through YC in W18 (https://news.ycombinator.com/item?id=16569534). EnvKey is an end-to-end encrypted configuration and secrets manager. It protects your organization's API keys, encryption keys, credentials, and other secrets, and makes it easy to run servers, scripts, tests, and everything else with the latest config. It also helps you avoid duplication in your…
2022 · v2.envkey.com · its alternatives →
- 7

When I came across a study that traced 4.5 million fake GitHub stars, it confirmed a suspicion I’d had for a while: stars are noisy. The issue is they’re visible, they’re persuasive, and they still shape hiring decisions, VC term sheets, and dependency choices—but they say very little about actual quality. I wrote StarGuard to put that number in perspective based on my own methodology inspired with what they did and to fold a broader supply-chain check into one command-line run. It starts with the simplest raw input: every starred_at timestamp GitHub will give. It applies a…
2025 · github.com · its alternatives →
- 8GM
2017 · gitmonkey.io · its alternatives →
- 9

Develop faster, eliminate complexity, protect your secrets
2022 · 1password.com · its alternatives →
- 10
 keychains.dev▲177
Hi HN — I’m a heavy OpenClaw user and, like many others, I’ve been thinking about how to give these new “unleashed” agents secure access to my accounts. Agents need API access to be useful. But API keys are long-lived secrets. And agents are not secure environments. So I built something for myself that quickly turned into a product: keychains.dev. The idea is simple: agents never see raw credentials. With Keychains.dev: • Agents make API calls via a drop-in replacement for curl or JavaScript’s fetch() • They use template variable names instead of embedding credentials • The request is…
Feb 2026 · keychains.dev · its alternatives →
- 11

Hi Hacker News! Shahar and Tal from Keep here. A few months ago, we introduced here at HN (https://news.ycombinator.com/item?id=34806482) Keep as an “open source alerting CLI” and got some interesting feedback - mainly around UI, automation, and supporting more tools. We were VERY early back then, and we understood that although the current DX around creating alerts is not great, it's not that critical and developers don’t need another tool just for that. But we did find something else. While talking to developers and devops, we found that a lot of companies use many tools…
2023 · github.com · its alternatives →
- 12

- 13

- 14IB
2024 · securelog.com · its alternatives →
- 15
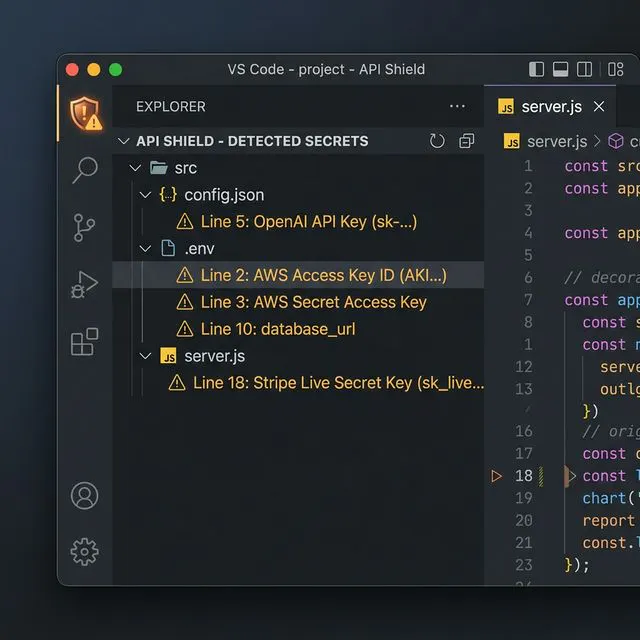
API Key & Secret Leak Detector
Mar 2026 · marketplace.visualstudio.com · its alternatives →
- 16

Open sourced application to detect security vulnerabilities.
2020 · github.com · its alternatives →
- 17
- 18WG
For the past month, we've been monitoring GitHub's public event stream to catch spam comments and fake stars. Today, the spammers are back. Go check out the damage! You can see the spam comments and which users are posting the spam in real time. Also, here's a post we wrote about how we set it up: https://www.trytrench.com/blog/preventing-spam-and-fake-star...
2024 · play.trytrench.com · its alternatives →
- 19
Catch exposed API keys and secrets while you browse
Jul 2026 · its alternatives →
- 20

Find exposed .env files in your GitHub repos instantly
Apr 2026 · scan-guard-io.lovable.app · its alternatives →
- 21
- 22WT
2016 · android.fallible.co · its alternatives →
- 23

Track leakage of your source code/data. FREE forever
2019 · its alternatives →
- 24PS
Hey HN, it's Farrukh and Umar. We're building listen.dev–a tool for proactive security monitoring in GitHub Actions to secure software releases from supply chain threats. Why we built this: As friends and collaborators for over a decade, we've been working on various startup ideas in dev tools and infrastructure. In 2017, while building an ML ops toolkit on Kubernetes, we got hacked. During a pilot with a fintech customer, our cluster became victim to a crypto-jacking attack. As it turned out, a dependency in our container base image contained malware (a Monero miner) which triggered inside…
2024 · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →