AI · alternatives · 2026

24 alternatives to Hosting 100 Linux dev environments on one VM using LXC
Open-source agent runtime — SSH-native isolation, eBPF egress policy, Kubernetes + LXC backends, GPU passthrough, MCP-native CLI - FootprintAI/Containarium
This project demonstrates how to run 100 Linux development environments simultaneously on a single virtual machine using LXC containerization. It is designed for developers and system administrators who need to… Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

hey guys. the other day i was migrating hosting providers and i just needed something not too heavy and convenient to spin up my backups for awhile and realised there is almost nothing out there. kimchi hasn't been updated for years and cockpit is heavy. so here's something i came up with in a couple hours because of a sudden urge, nothing fancy just basic creation with cloud init, lifecycle management and image/storage, but it's modern-ish and it compiles to a 8.4mb binary inclusive of the embedded web UI, CLI and API, and only dep is libvirt.
2025 · github.com · its alternatives →
- 2
 Cerebrium▲300
If you haven’t noticed, GPUs are scarce right now. The global boom in inference has demand growing faster than supply can keep up, and at Cerebrium ...
2024 · cerebrium.ai · its alternatives →
- 3

Hi HN - We've been working on Coasts (“containerized hosts”) to make it so you can run multiple localhost instances, and multiple docker-compose runtimes, across git worktrees on the same computer. Here’s a demo: https://www.youtube.com/watch?v=yRiySdGQZZA. There are also videos in our docs that give a good conceptual overview: https://coasts.dev/docs/learn-coasts-videos. Agents can make code changes in different worktrees in isolation, but it's hard for them to test their changes without multiple localhost runtimes that are isolated and scoped to those…
Mar 2026 · github.com · its alternatives →
- 4

I've been working on CloudRouter, a skill + CLI that gives coding agents like Claude Code and Codex the ability to start cloud VMs and GPUs. When an agent writes code, it usually needs to start a dev server, run tests, open a browser to verify its work. Today that all happens on your local machine. This works fine for a single task, but the agent is sharing your computer: your ports, RAM, screen. If you run multiple agents in parallel, it gets a bit chaotic. Docker helps with isolation, but it still uses your machine's resources, and doesn't give the agent a browser, a desktop, or a GPU to…
Feb 2026 · cloudrouter.dev · its alternatives →
- 5

Shuru is a lightweight sandbox that spins up Linux VMs on macOS using Apple's Virtualization.framework. Boots in about a second on Apple Silicon, and everything is ephemeral by default. There's a checkpoint system for when you do want to persist state, and sandboxes run without network access unless you explicitly allow it. Single Rust binary, no dependencies. Built it for sandboxing AI agent code execution, but it works well for anything where you need a disposable Linux environment.
Feb 2026 · shuru.run · its alternatives →
- 6BI
Self-hosted virtual machines for background coding agents.
Jun 2026 · bastion.computer · its alternatives →
- 7

Create microVMs from OCI images. Contribute to slp/krunvm development by creating an account on GitHub.
2021 · github.com · its alternatives →
- 8WM
Try it out! https://glhf.chat/ Hey HN! We’ve been working for the past few months on a website to let you easily run (almost) any open-source LLM on autoscaling GPU clusters. It’s free for now while we figure out how to price it, but we expect to be cheaper than most GPU offerings since we can run the models multi-tenant. Unlike Together AI, Fireworks, etc, we’ll run any model that the open-source vLLM project supports: we don’t have a hardcoded list. If you want a specific model or finetune, you don’t have to ask us for it: you can just paste the Hugging Face link in and…
2024 · glhf.chat · its alternatives →
- 9

I've built this to make it easy to host your own infra for lightweight VMs at large scale. Intended for exec of AI-generated code, for CICD runners, or for off-chain AI DApps. Mainly to avoid Docker-in-Docker dangers and mess. Super easy to use with CLI / Python SDK, friendly to AI engs who usually don't like to mess with VM orchestration and networking too much. Defense-in-depth philosophy. Would love to get feedback (and contributors: clear & exciting roadmap!), thx
Oct 2025 · github.com · its alternatives →
- 10

An on-premises, bare-metal solution for deploying GPU-powered applications in containers - emergingstack/es-dev-stack
2016 · github.com · its alternatives →
- 11

Spin up secure sandboxes in ~100 ms
Nov 2025 · hopx.ai · its alternatives →
- 12
 Vxero Neo▲74
SSH-native CLI that manage servers, apps, infrastructure
Apr 2026 · neo.vxero.dev · its alternatives →
- 13
 Keystone▲125
We kept hitting the same wall: you clone some arbitrary repo and just want it to run without any configuration work. So we built Keystone, an open source tool that spins up a Modal sandbox, runs Claude Code inside it, and produces a working .devcontainer/ config (Dockerfile, devcontainer.json, test runner) for any git repo. We build on the dev container standard, so the output works with VS Code and GitHub Codespaces out of the box. Main use cases: reproducible dev/CI environments, self-describing repos, and safely sandboxed coding agents. Our goal is to encourage all repos to…
Mar 2026 · github.com · its alternatives →
- 14
 1DevTool▲94
Multi-project IDE with persistent terminals and 9 dev tools
Mar 2026 · 1devtool.com · its alternatives →
- 15
 SuperHQ▲95
Hey HN, I built SuperHQ, an app that lets you run coding agents in local sandboxes (powered by Shuru). No custom UI wrapping the agents, they run as CLI/TUI like they were designed to. It just provides you the tools most of us (okay, maybe just me?) needed for running multiple coding agents in parallel without worrying about breaking your system or work environment. Each agent runs in its own microVM. You mount your projects in, writes go to a tmpfs overlay so your host is never touched, and you get a unified diff view to accept or discard changes. API keys never enter the sandbox, they…
Apr 2026 · superhq.ai · its alternatives →
- 16

A fast, rootless sandbox and virtual resource runtime for any workload, including untrusted and AI-generated code. Daemonless: a real, kernel-enforced container in ~3.5 ms from an OCI image, out of one static binary - getkern/kern
Aug 2026 · github.com · its alternatives →
- 17

Hi HN! We’re Yann, Edouard, and Bastien from Koyeb (https://www.koyeb.com/). We’re building a platform to let you deploy full-stack apps on high-performance hardware around the world, with zero configuration. We provide a “global serverless feeling”, without the hassle of re-writing all your apps or managing k8s complexity [1]. We built Scaleway, a cloud service provider where we designed ARM servers and provided them as cloud servers. During our time there, we saw customers struggle with the same issues while trying to deploy full-stack applications and APIs resiliently. As…
2023 · koyeb.com · its alternatives →
- 18

Hi HN, we built SuperHQ, an open source app that runs AI coding agents in isolated microVM sandboxes instead of directly on your machine. Each agent gets its own VM with a full Debian environment. You mount your projects in, writes go to a tmpfs overlay so your host is never touched, and you get a diff view to accept or discard changes. API keys never enter the sandbox. We also just launched remote.superhq.ai which acts as a remote control for SuperHQ, allowing you to access your workspaces and agents from anywhere.
Apr 2026 · github.com · its alternatives →
- 19
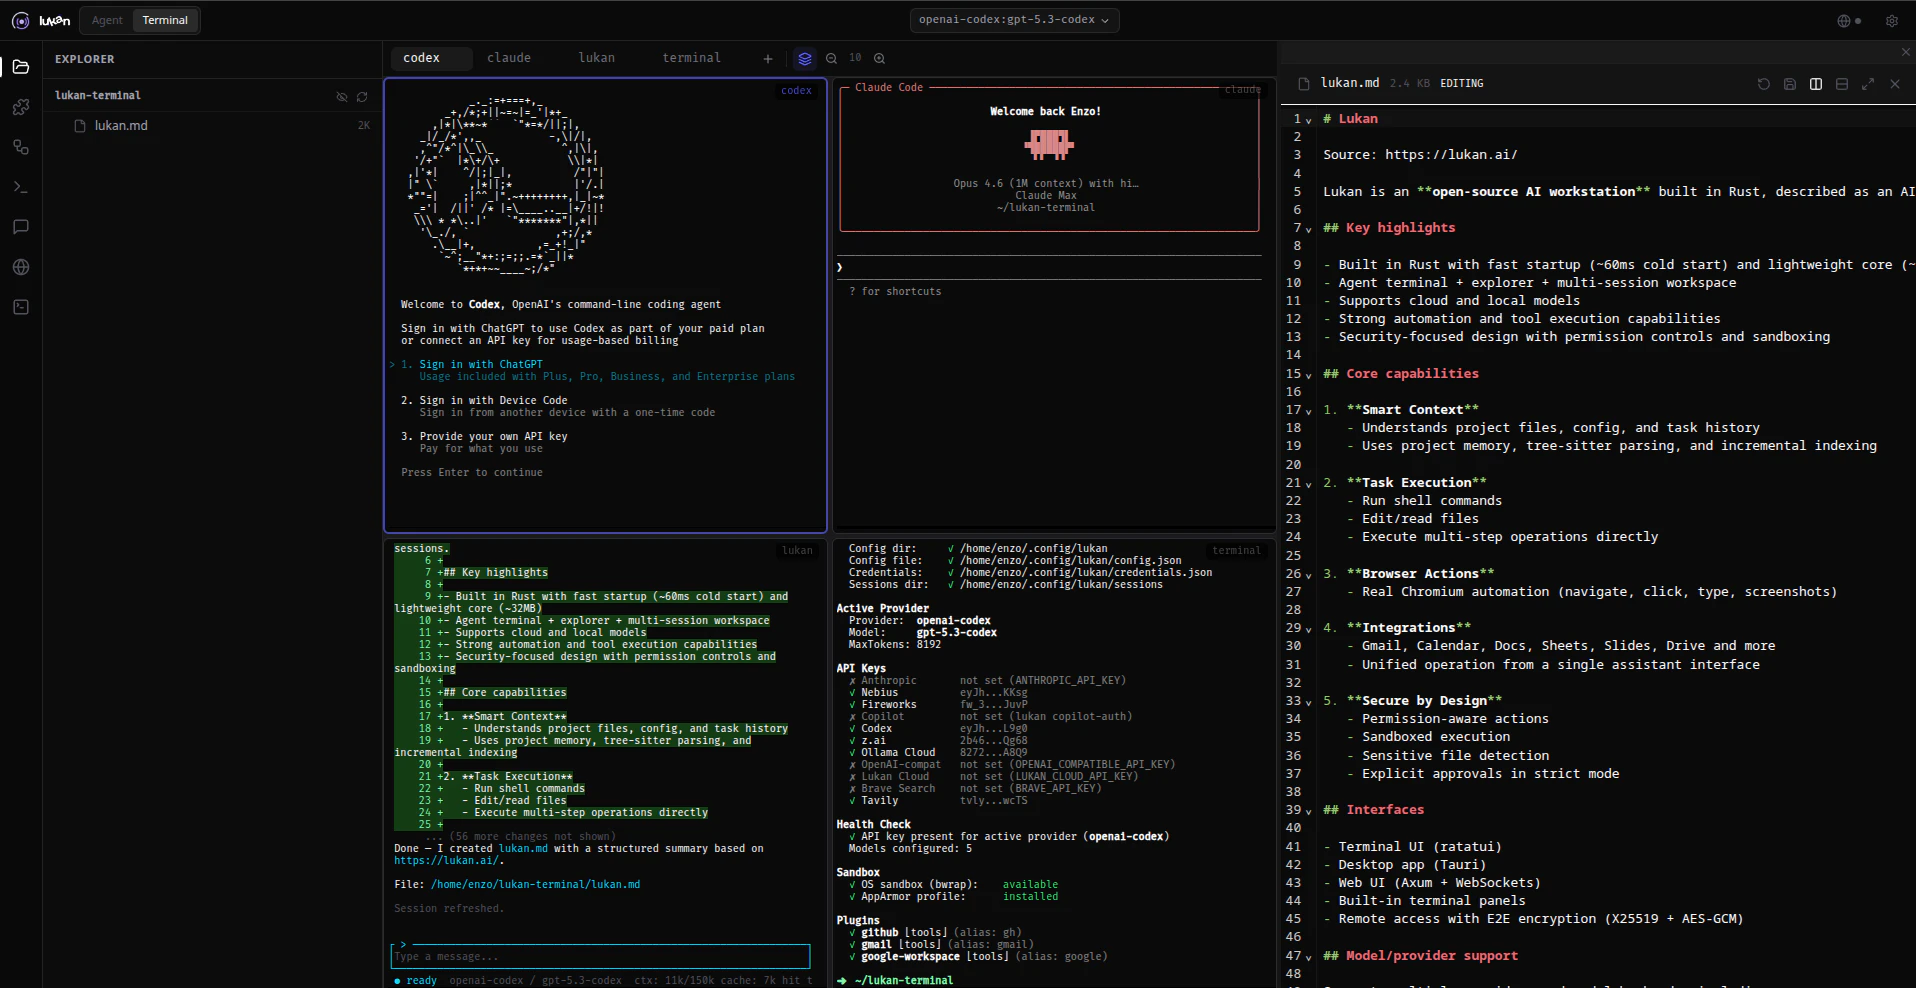
Hi HN, I've been building Lukan, an open-source (MIT) agentic workstation that runs entirely as a single Rust binary with zero runtime dependencies. I started this because I wanted a unified workstation optimized for my own productivity. My goal was to build an environment where I could securely remote into my machine from anywhere, seamlessly view and modify local files, and run AI agents or drop into a terminal side-by-side, all integrated with a rich set of built-in tools. Here is what makes it different: Multi-agent sessions: Run multiple agents in parallel, each with its own isolated…
Apr 2026 · lukan.ai · its alternatives →
- 20LV
Hello HN! We've been working on a new hypervisor https://kwarantine.xyz that can run strongly isolated containers. This is still a WIP, but we wanted to give the community an idea about our approach, its benefits, and various use cases it unlocks. Today, VMs are used to host containers, and make up for the lack of strong security as well as kernel isolation in containers. This work adds this missing security piece in containers. We plan on launching a free private beta soon. Meanwhile, we'd deeply appreciate any feedback, and happy to answer any questions here or on our slack…
2021 · its alternatives →
- 21

I got tired of libvirt XML and Vagrant's Ruby/reload dance for single-host VM stacks, so I built a compose-style runtime directly on QEMU/KVM. What's there: GPU passthrough as a first-class primitive (VFIO, OVMF, per-instance EFI vars), healthchecks that gate depends_on over SSH, socket-multicast L2 between VMs with no root and no bridge config, cloud-init wired through the YAML, Dockerfile support for provisioning. What it's not: Kubernetes. No clustering, no live migration, no control plane. Single host. Prototype, but I'm running it on real hardware. Curious what breaks for…
Apr 2026 · github.com · its alternatives →
- 22RC
Hi HN, this is Cesar and Rodny, developers of an open-source container runtime called Sysbox, and co-founders of a startup called Nestybox (YC S20). We launched on HN almost a year ago and got excellent feedback then (https://news.ycombinator.com/item?id=24084758). Happy to say that over the past year, Sysbox has continued to gain traction, particularly for securing containers in production, CI/CD, and containerized dev environments. We wanted to announce an important new feature: integration between Sysbox and Kubernetes. As a quick refresher, Sysbox is a "runc" that…
2021 · its alternatives →
- 23
 Linchpin▲74
Open-source, self-hostable runtime for managed AI agents
May 2026 · linchpin.work · its alternatives →
- 24

Hi HN, I've been building Nucleus, a lightweight Linux container runtime focused on two workloads: ephemeral AI-agent sandboxes and declarative NixOS services. It's a single Rust binary, no daemon. It is not a Docker replacement and not a strict subset of Docker either. I dropped the entire image-and-distribution half (no Dockerfile, no layers, no registry, no pull/push, no persistent storage layer) in exchange for going deeper on isolation and reproducibility. The rootfs is either a directory copied into tmpfs (agent mode) or a Nix-built closure mounted read-only (production mode). If…
Jun 2026 · github.com · its alternatives →
Also compare
- Lightweight tool for managing Linux virtual machines alternatives
- Cerebrium alternatives
- Coasts – Containerized Hosts for Agents alternatives
- Skill that lets Claude Code/Codex spin up VMs and GPUs alternatives
- Local-First Linux MicroVMs for macOS alternatives
- Bastion – isolated Linux VMs for background coding agents alternatives
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →