Dev tools · alternatives · 2026
24 alternatives to MCP Guard
The firewall for AI agents. Block dangerous commands
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1
 MCP Defender▲152
Hi HN, MCP Defender is an open source desktop app that automatically proxies your MCP traffic in AI apps like Cursor, Claude, Windsurf and VSCode. It then scans all requests and responses between the apps and the MCP tools they call. If it detects anything malicious, it alerts you and lets you allow or block the tool call. While the threat landscape of MCP is still being actively researched, there are dangerous things that MCP Defender can block today. For example, a developer asks Cursor to fix a Github issue with an attached crash log. However, the Github issue was created by an attacker…
2025 · mcpdefender.com · its alternatives →
- 2

- 3

- 4

Firewall for AI agents. Scan before you trust.
Mar 2026 · aisecurityguard.io · its alternatives →
- 5

Runtime firewall for AI coding agents.
Aug 2026 · contextfence.dev · its alternatives →
- 6

Give AI agents access to real-time data across 200+ apps
May 2026 · apideck.com · its alternatives →
- 7
 LockIn MCP▲116
I was tired of how bad distraction blockers are so I built my own. LockIn lets AI assistants (Claude, ChatGPT, Cursor, etc.) block websites by editing the system hosts file directly via MCP tools (via a secure cloudflare bridge). Why? Because chrome extensions don't work. Blocking it natively makes it unbypassable, and having your agent gatekeep your focus is the ultimate cheat code. Since everyone is using AI agents nowadays, but most people start scrolling or Reddit while waiting for Claude Code to finish, giving them control over your focus solves that. The MCP server exposes four tools:…
Jun 2026 · lockinmcp.com · its alternatives →
- 8
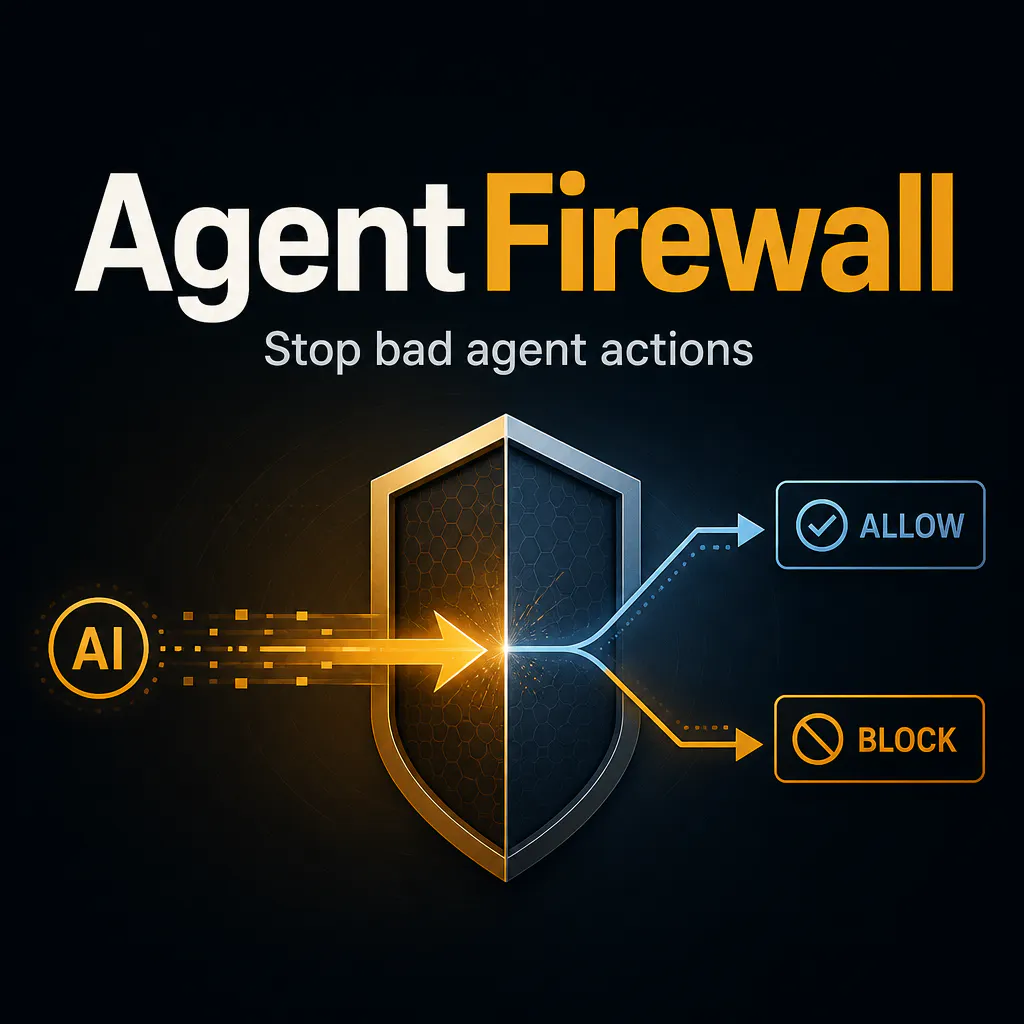
Project AI agents from unsafe actions before they execute.
Aug 2026 · agentfirewall.launchreadyal.com · its alternatives →
- 9
Security firewall for AI agents. Cloudflare for MCP.
Feb 2026 · agent-wall.github.io · its alternatives →
- 10

Hi HN, Gabriel, Co-Founder at Permit.io. We're releasing Permit MCP Gateway today, an authorization proxy for MCP servers. TL;DR - we built an MCP Gateway that developers love and CISOs trust. Watch more[0] Now, after your little hate on using fancy copy on HN, to the real thing: MCP is in a strange place. Developers are debating whether it's overcomplicated compared to CLIs or skills files. Meanwhile, enterprises are adopting it by default because every agentic system that acts on your behalf, Cursor, Claude, Copilot, internal agents, needs a stable infrastructure for connecting to tools.…
Mar 2026 · permit.io · its alternatives →
- 11
 CtrlAI▲104
Transparent proxy that secures AI agents with guardrails
Mar 2026 · github.com · its alternatives →
- 12

I noticed the growing security concerns around MCP (https://news.ycombinator.com/item?id=43600192) and built an open source tool that can detect several patterns of tool poisoning attacks, exfiltration channels and cross-origin manipulations. MCP-Shield scans your installed servers (Cursor, Claude Desktop, etc.) and shows what each tool is trying to do at the instruction level, beyond just the API surface. It catches hidden instructions that try to read sensitive files, shadow other tools' behavior, or exfiltrate data. Example of what it detects: - Hidden instructions…
2025 · github.com · its alternatives →
- 13

At Deno we've been using OpenClaw and other agents increasingly for addressing production problems in Deno Deploy - when a PagerDuty alert fires, the agent starts researching the cause and making fixes. In order to do this, the agent needs access to real production systems - postgres, kubernetes, gcp, clickhouse, github, etc. But this is dangerous to say the least - we want destructive actions to be reviewed by other LLMs, approved by humans, and logged appropriately. Claw Patrol terminates TCP connections over WireGuard or Tailscale, then parses application protocols (eg http, postgres,…
Jun 2026 · github.com · its alternatives →
- 14

Hey everyone, I've wanted an easy way to control which mcp server tools are available to clients. So for example, I might want a gmail server to only expose the read tool (but not send, delete etc). I figured if I create a cli for spawning mcp servers, I could intercept the stdin, stdout, stderr etc and modify what the clients see when they are making calls to list tools, resources, and prompts. Well it worked! In the initial version you can easily add a server to claude with a safe list of tools: npx -y mcpgod add @modelcontextprotocol/server-everything --client claude --tools=echo,add…
2025 · github.com · its alternatives →
- 15

Hi HN, We’re building security tooling around agentic AI systems. Today, we're releasing our public MCP catalog with detailed risk analysis for every MCP server we've found on the internet: https://mcp.armor1.ai/mcp-directory We all love agents and the power that MCPs unlock: suddenly your AI assistant can query databases, manage files, call APIs, and interact with the real world. But when we started adopting MCPs ourselves, we kept running into the same nagging questions: Is this MCP safe? Where is my data actually going? Could it execute destructive actions? Is it…
Feb 2026 · mcp.armor1.ai · its alternatives →
- 16

Background: I've been working on agentic guardrails because agents act in expensive/terrible ways and something needs to be able to say "Maybe don't do that" to the agents, but guardrails are almost impossible to enforce with the current way things are built. Context: We keep running into so many problems/limitations today with MCP. It was created so that agents have context on how to act in the world, it wasn't designed to become THE standard rails for agentic behavior. We keep tacking things on to it trying to improve it, but it needs to die a SOAP death so REST can rise in it's…
Mar 2026 · github.com · its alternatives →
- 17
 ContextGuard▲12
I built ContextGuard after discovering that 43% of MCP servers have critical security vulnerabilities. MCP (Model Context Protocol) is the new standard that lets Claude Clients(Desktop, Windsurf, Cursor, etc.) access external tools and data sources - think of it as a plugin system for AI assistants. The problem: When you give those clients access to your filesystem, databases, or APIs through MCP servers, you're opening up serious attack vectors. Prompt injection, data leakage, and path traversal attacks are all possible. Most developers building MCP servers don't have security expertise,…
2025 · github.com · its alternatives →
- 18

- 19
AI-powered firewall that instantly blocks malicious Web3.
Jul 2026 · guardfast.vercel.app · its alternatives →
- 20

- 21

Local security & compliance scanner for AI agents
Jul 2026 · safeclaude.net · its alternatives →
- 22

cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls. - agentrust-io/cmcp
Aug 2026 · github.com · its alternatives →
- 23

Block bad command execution and keep you away from danger.
May 2026 · github.com · its alternatives →
- 24
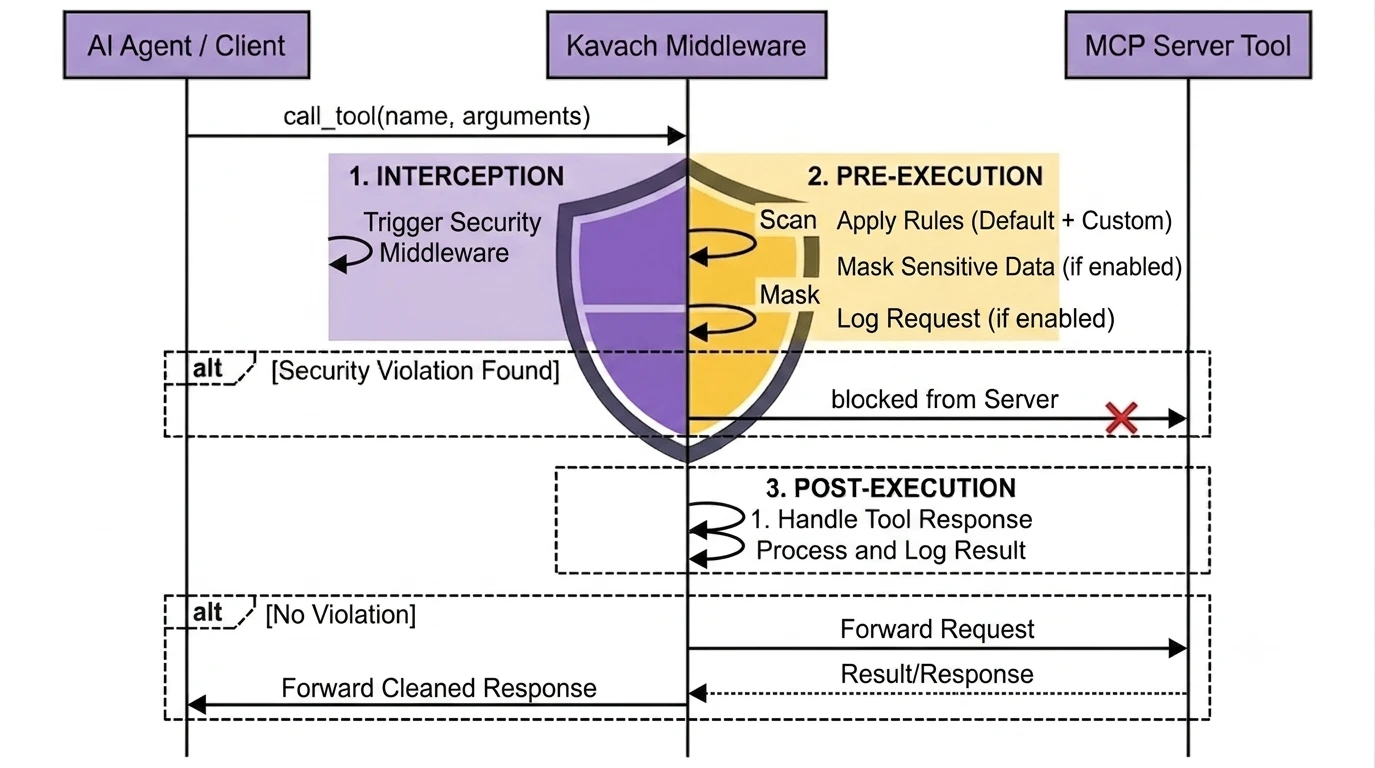
Security middleware for AI agents and MCP servers
Jun 2026 · pypi.org · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →