Life & fun · alternatives · 2026
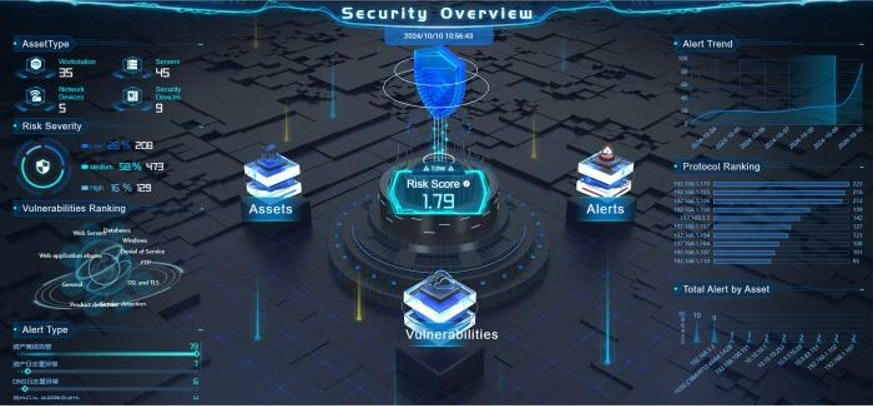
24 alternatives to Secisland SOC
log audit,UEBA,SPL,SOAR,asset management
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1
 Secure Audit Log▲272
Log important application events with a single line of code
2023 · pangea.cloud · its alternatives →
- 2

Track every critical event within your product
2023 · boxyhq.com · its alternatives →
- 3

Let your customers set up enterprise SSO & audit logs easily
2023 · ory.com · its alternatives →
- 4

- 5

- 6
 Exploit Alarm▲151
Vulnerability intelligence for real-time threat analysis
2024 · exploitalarm.com · its alternatives →
- 7EY
2019 · secalerts.co · its alternatives →
- 8
 SSOReady▲144
Open source developer tools for enterprise single sign-on
2024 · github.com · its alternatives →
- 9

Build automated workflows tailored for data teams
2024 · secoda.co · its alternatives →
- 10

- 11

Hi HN! We’re Ethan and Danny, the authors of Tangent (https://github.com/telophasehq/tangent), a Rust-based log pipeline where all normalization, enrichment, and detection logic runs as WASM plugins. We kept seeing the same problems in the OCSF (https://ocsf.io) community: 1) Schemas change constantly. Large companies have whole teams dedicated to keeping vendor→OCSF mappings up to date. 2) There’s no shared library of mappings, so everyone recreates the same work. 3) Writing mappers is tedious, repetitive work. 4) Most pipelines use proprietary DSLs that are…
Nov 2025 · github.com · its alternatives →
- 12

Contribute to Park07/amradio development by creating an account on GitHub.
Feb 2026 · github.com · its alternatives →
- 13

- 14
SaaS to secure your fleet of machines.
2019 · sttor.com · its alternatives →
- 15
Integrated Risk Based Vulnerability Management platform
2022 · seconize.co · its alternatives →
- 16

🔥 A fully open source audit logs service and embeddable UI easily deployed to your own Kubernetes cluster. Brought to you by replicated.com and boxyhq.com 🚀 - retracedhq/retraced
2023 · github.com · its alternatives →
- 17

AI-first incident radar for noisy mainframe logs
Dec 2025 · hazel-rudbeckia-fa4.notion.site · its alternatives →
- 18
- 19
 Heeler▲13
Shift left with context: ASPM, SCA, Runtime Threat Modeling
2024 · heeler.com · its alternatives →
- 20
 Guardius▲14
Unified platform for security, performance, and monitoring
2024 · guardius.io · its alternatives →
- 21

Hello HN. I'm Maxime, founder at LimaCharlie (https://limacharlie.io), a Hyperscaler for SecOps (access building blocks you need to build security operations, like AWS does for IT). We’ve engineered a new product on our platform that solves a timely issue acting as a guardrail between your AI and the world: Viberails (https://www.viberails.io) This won't be new to folks here, but we identified 4 challenges teams face right now with AI tools: 1. Auditing what the tools are doing. 2. Controlling toolcalls (and their impact on the world). 3. Centralized management. 4. Easy…
Feb 2026 · viberails.io · its alternatives →
- 22

Enterprise SIEM + SOAR for startups
Feb 2026 · github.com · its alternatives →
- 23

Hi HN, I'm Robel. I built LogClaw because I was tired of paying for Datadog and still waking up to pages that said "something is wrong" with no context. LogClaw is an open-source log intelligence platform that runs on Kubernetes. It ingests logs via OpenTelemetry and detects anomalies using signal-based composite scoring — not simple threshold alerting. The system extracts 8 failure-type signals (OOM, crashes, resource exhaustion, dependency failures, DB deadlocks, timeouts, connection errors, auth failures), combines them with statistical z-score analysis, blast radius, error velocity, and…
Mar 2026 · logclaw.ai · its alternatives →
- 24
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →