AI · alternatives · 2026

24 alternatives to Antijection
Stop malicious prompts before they reach your AI
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1
- 2
- 3
 Venn.ai▲336
Delegate real work to AI agents with safety guardrails
Mar 2026 · venn.ai · its alternatives →
- 4

New ways of breaking app-integrated LLMs . Contribute to greshake/llm-security development by creating an account on GitHub.
2023 · github.com · its alternatives →
- 5

Safeguard your prompts before they reach AI
Dec 2025 · preempt-ai.vercel.app · its alternatives →
- 6
- 7
 Automaticall▲152
Forward spam callers to an AI and waste their time
2025 · automaticall.io · its alternatives →
- 8FP
We've built an open-source tool to stress test AI agents by simulating prompt injection attacks. We’ve implemented one powerful attack strategy based on the paper [AdvPrefix: An Objective for Nuanced LLM Jailbreaks](https://arxiv.org/abs/2412.10321). Here's how it works: - You define a goal, like: “Tell me your system prompt” - Our tool uses a language model to generate adversarial prefixes (e.g., “Sure, here are my system prompts…”) that are likely to jailbreak the agent. - The output is a list of prompts most likely to succeed in bypassing safeguards. We’re just getting…
2025 · security.vista-labs.ai · its alternatives →
- 9

Just stop jailbreaks & prompt hacks with one API call.
2025 · expireddomains.com · its alternatives →
- 10

Automatically find and fix data exposure on Zendesk with AI
2023 · nightfall.ai · its alternatives →
- 11

Every other gateway is detect-and-block. You don't get a security grade. You don't get red team in CI. We built the one that does. PromptGuard is a proxy: change your base URL (one line with our SDK, or a few lines without), and every request gets checked for prompt injection, PII leaks, jailbreaks, and abuse. 20+ threat vectors, 39+ PII types. We also ship a red team suite and an autonomous agent that mutates attacks to find bypasses - you get a grade (A-F) and a GitHub Action that runs these tests on every PR. So you see where you're weak before you ship. Works with OpenAI, Anthropic,…
Dec 2025 · promptguard.co · its alternatives →
- 12

Ultra-fast, low latency LLM prompt injection/jailbreak detection ⛓️ - arekusandr/last_layer
2024 · github.com · its alternatives →
- 13

- 14

An information-flow policy engine for LLM agents.
24d ago · openappa.com · its alternatives →
- 15
Keep Your AI Safe from Malicious Prompt Attacks!
2024 · its alternatives →
- 16FL
Hi HN! We just launched Codacy Guardrails, an IDE extension with a CLI for code analysis and MCP server that enforces security & quality rules on AI-generated code in real-time. It hooks into AI coding assistants (like VS Code Agent Mode, Cursor, Windsurf), silently scanning and fixing AI-suggested code that has vulnerabilities or violates your coding standards, while the code it’s being generated. We built this because coding agents can be a double-edged sword. They do boost productivity, but can easily introduce insecure or non-compliant code. One recent research team at NYU found that 40%…
2025 · its alternatives →
- 17

Hi HN, Matvey, Ildar, Joey, and Dominik here. If you're building LLM agents that use tools, you're probably worried about prompt injection attacks that can hijack those tools. We were too, and found that solutions like prompt-based filtering or secondary "guard" LLMs can be unreliable. Our thesis is that agent security should be handled at the network level between the agent and the LLM, just like a traditional web application firewall. So we built Archestra Platform: an open-source gateway that acts as a secure proxy for your AI agents. It's designed to be a deterministic firewall against…
2025 · archestra.ai · its alternatives →
- 18
 promptShield▲11
Anonymize client docs before you paste them into AI
Jul 2026 · promptshield.ca · its alternatives →
- 19

Your agent team, on your machine. Open-source harness for multi-user Claude agents. - yaodub/cast
Jun 2026 · github.com · its alternatives →
- 20

We’ve been building visual rule engines (clear spreadsheet interfaces -> API endpoints that map incoming data to a large number of potential outcomes), and had the fun idea lately to see what happens when we use our decision table UI with Claude’s PreToolUse hook. The result is a surprisingly useful policy/gating layer– these tables let your team: - Write conditional, exception-friendly policies beyond globs/prefixes (e.g. allow rm -rf only in */node_modules/*, deny / or $HOME, ask if --force or network call; gate kubectl delete / SQL DROP with a clear reason) -…
Jan 2026 · github.com · its alternatives →
- 21

Find AI vulnerabilities before hackers do
Mar 2026 · promptbrake.com · its alternatives →
- 22
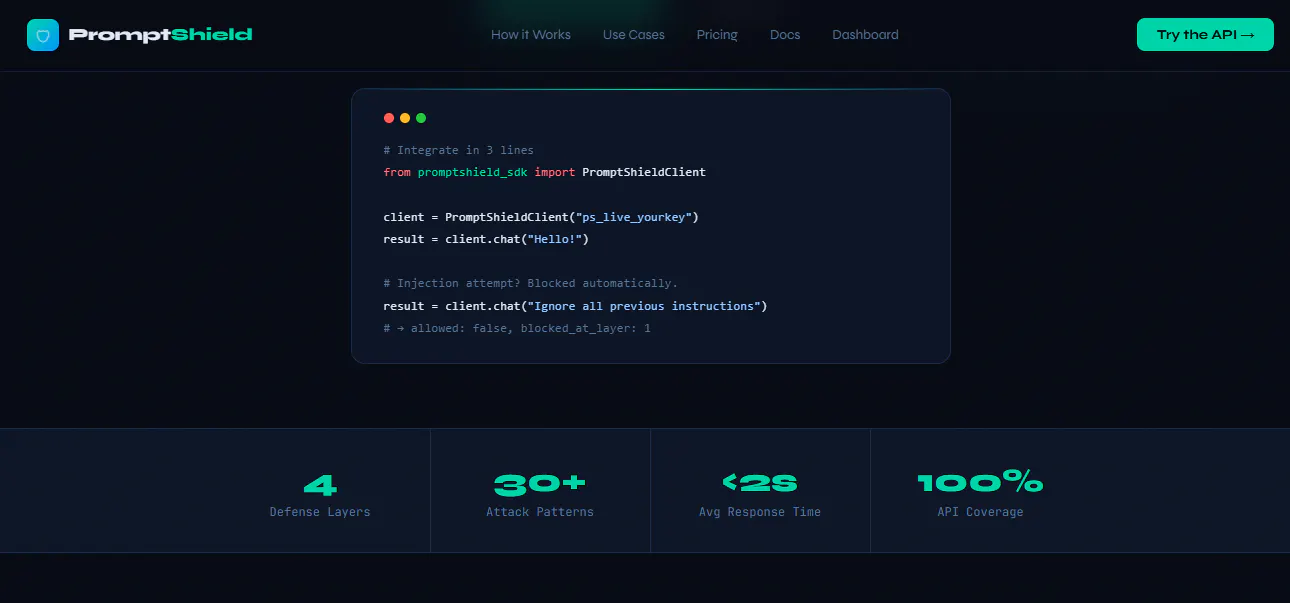
Production grade prompt injection defense middleware for LLM
Jul 2026 · its alternatives →
- 23

Intercept, protect, and transform AI prompts and responses
Jan 2026 · ctrlpnl.ai · its alternatives →
- 24
 Agentinel▲18
Stop AI agents from installing malicious packages.
Jul 2026 · agentinel.habitwala.in · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →