AI · alternatives · 2026

24 alternatives to Golf
The enterprise firewall for MCP providers
Golf Firewall is a security layer designed for enterprises that expose MCP servers. It protects these servers from malicious requests and data breaches by blocking prompt injections, personally identifiable information… Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1

🛡️ Open-source and cloud-native Web Application Firewall (WAF) - bunkerity/bunkerweb
2024 · github.com · its alternatives →
- 2

Documentation of BunkerWeb, the open source and next generation WAF.
2025 · docs.bunkerweb.io · its alternatives →
- 3

I noticed the growing security concerns around MCP (https://news.ycombinator.com/item?id=43600192) and built an open source tool that can detect several patterns of tool poisoning attacks, exfiltration channels and cross-origin manipulations. MCP-Shield scans your installed servers (Cursor, Claude Desktop, etc.) and shows what each tool is trying to do at the instruction level, beyond just the API surface. It catches hidden instructions that try to read sensitive files, shadow other tools' behavior, or exfiltrate data. Example of what it detects: - Hidden instructions…
2025 · github.com · its alternatives →
- 4
 FireWally▲156
A free Mac firewall powered by Apple Intelligence
Dec 2025 · apps.apple.com · its alternatives →
- 5

Hi HN, Gabriel, Co-Founder at Permit.io. We're releasing Permit MCP Gateway today, an authorization proxy for MCP servers. TL;DR - we built an MCP Gateway that developers love and CISOs trust. Watch more[0] Now, after your little hate on using fancy copy on HN, to the real thing: MCP is in a strange place. Developers are debating whether it's overcomplicated compared to CLIs or skills files. Meanwhile, enterprises are adopting it by default because every agentic system that acts on your behalf, Cursor, Claude, Copilot, internal agents, needs a stable infrastructure for connecting to tools.…
Mar 2026 · permit.io · its alternatives →
- 6

Skip migration and launch MCP with built-in Auth
Nov 2025 · arcade.dev · its alternatives →
- 7
 MCP Playground▲160
MCP Playground is a Postman-style tool for MCP — inspect servers, execute tools live, test your client, all from the browser. Four things in one place: 1. Free hosted MCP servers — four public test servers anyone can point their client at: Echo (connectivity), Auth (Bearer token flow), Error (error handling), Complex (multi-tool schemas).No sign-up, just use the URL. 2. Server inspector — paste any remote MCP server URL, see all its tools/resources/prompts, execute them live, inspect the full JSON-RPC log. HTTP, SSE, and WebSocket all supported. 3. Registry — 10,000+ servers…
Nov 2025 · mcpplayground.io · its alternatives →
- 8

Hey HN, I built pg-mcp, a Model Context Protocol (MCP) server for PostgreSQL that provides structured schema inspection and query execution for LLMs and agents. It's multi-tenant and runs over HTTP/SSE (not stdio) Features - Supports multiple database connections from multiple agents - Schema Introspection: Returns table structures, types, indexes and constraints; enriched with descriptions from pg_catalog. (for well documented databases) - Read-Only Queries: Controlled execution of queries via MCP. - EXPLAIN Tool: Helps smart agents optimize queries before execution. - Extension…
2025 · github.com · its alternatives →
- 9
 MCP Defender▲152
Hi HN, MCP Defender is an open source desktop app that automatically proxies your MCP traffic in AI apps like Cursor, Claude, Windsurf and VSCode. It then scans all requests and responses between the apps and the MCP tools they call. If it detects anything malicious, it alerts you and lets you allow or block the tool call. While the threat landscape of MCP is still being actively researched, there are dangerous things that MCP Defender can block today. For example, a developer asks Cursor to fix a Github issue with an attached crash log. However, the Github issue was created by an attacker…
2025 · mcpdefender.com · its alternatives →
- 10
 ContextGuard▲12
I built ContextGuard after discovering that 43% of MCP servers have critical security vulnerabilities. MCP (Model Context Protocol) is the new standard that lets Claude Clients(Desktop, Windsurf, Cursor, etc.) access external tools and data sources - think of it as a plugin system for AI assistants. The problem: When you give those clients access to your filesystem, databases, or APIs through MCP servers, you're opening up serious attack vectors. Prompt injection, data leakage, and path traversal attacks are all possible. Most developers building MCP servers don't have security expertise,…
2025 · github.com · its alternatives →
- 11
- 12

Free MCP for security AI: live BGP, DNS, threat graph
May 2026 · whisper.security · its alternatives →
- 13

Hi HN, We’re building security tooling around agentic AI systems. Today, we're releasing our public MCP catalog with detailed risk analysis for every MCP server we've found on the internet: https://mcp.armor1.ai/mcp-directory We all love agents and the power that MCPs unlock: suddenly your AI assistant can query databases, manage files, call APIs, and interact with the real world. But when we started adopting MCPs ourselves, we kept running into the same nagging questions: Is this MCP safe? Where is my data actually going? Could it execute destructive actions? Is it…
Feb 2026 · mcp.armor1.ai · its alternatives →
- 14

Hey everyone, I've wanted an easy way to control which mcp server tools are available to clients. So for example, I might want a gmail server to only expose the read tool (but not send, delete etc). I figured if I create a cli for spawning mcp servers, I could intercept the stdin, stdout, stderr etc and modify what the clients see when they are making calls to list tools, resources, and prompts. Well it worked! In the initial version you can easily add a server to claude with a safe list of tools: npx -y mcpgod add @modelcontextprotocol/server-everything --client claude --tools=echo,add…
2025 · github.com · its alternatives →
- 15

- 16
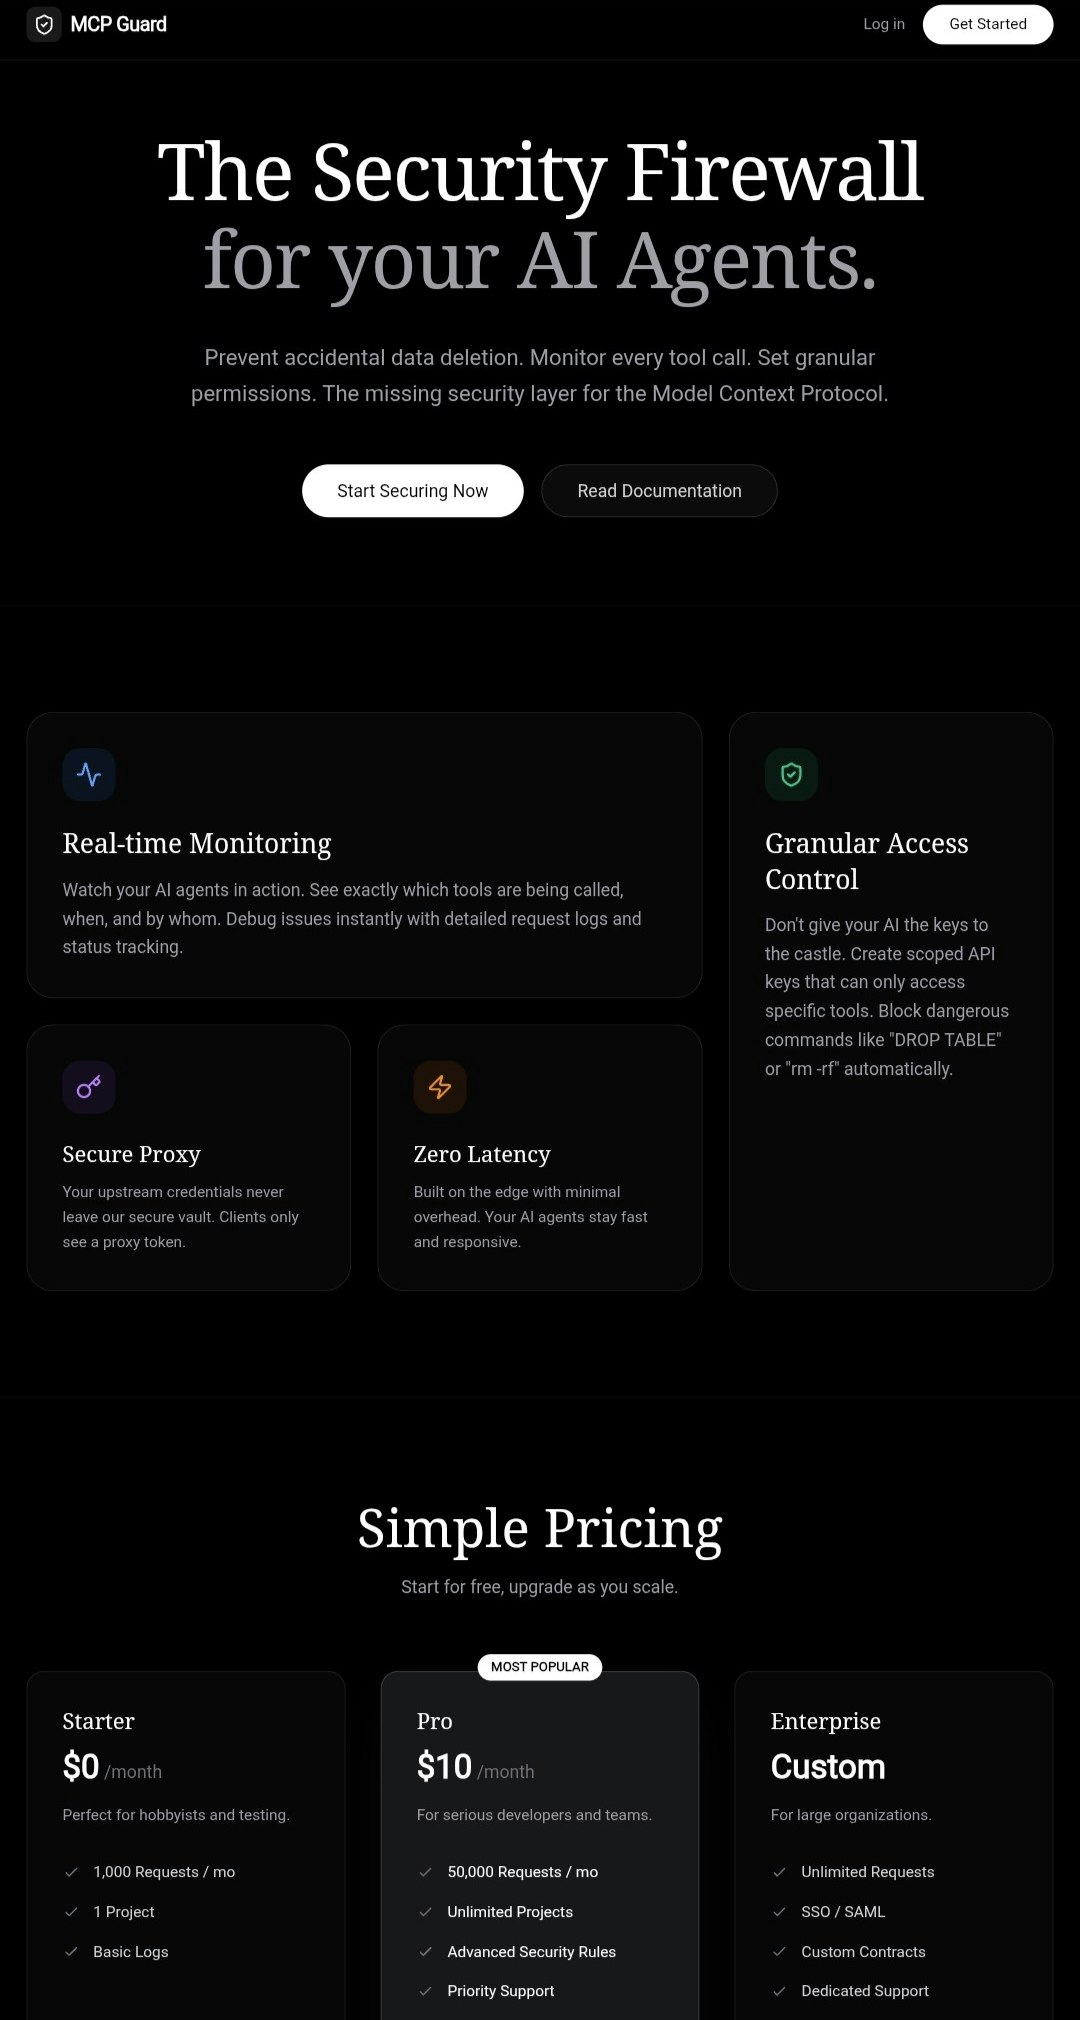
The firewall for AI agents. Block dangerous commands
Dec 2025 · mcp-shield.vercel.app · its alternatives →
- 17

At my last company, we connected Claude Code and Cursor to almost all our internal services via MCP. It made the team incredibly fast, but we hit a wall: permissions. If you give an agent "Read Only" access, it can’t actually fix anything. If you give it "Write" access, it’s only a matter of time before a hallucination or a bad prompt results in a deleted database or a nuked production bucket. We had a few "close calls" that convinced us that simply reducing IAM permissions makes agents useless. I built Armour (https://github.com/fuushyn/armour) to solve this. It’s a…
Jan 2026 · github.com · its alternatives →
- 18
Security firewall for AI agents. Cloudflare for MCP.
Feb 2026 · agent-wall.github.io · its alternatives →
- 19

Fool attackers and protect your web services with BunkerWeb, the open-source and next-gen Web Application Firewall (WAF).
Jan 2026 · bunkerweb.io · its alternatives →
- 20

SQL Firewall Extension for PostgreSQL. Contribute to uptimejp/sql_firewall development by creating an account on GitHub.
2015 · github.com · its alternatives →
- 21

To power the firewalling for our agents so that they couldn't contact arbitrary services, I build netfence. It's like Envoy but for eBPF filters. It allows you to define different DNS-based rules that are resolved in a local daemon to IPs, then pushed to the eBPF filter to allow traffic. By doing it this way, we can still allow DNS-defined rules, but prevent contacting random IPs. There's also no network performance penalty, since it's just DNS lookups and eBPF filters referencing memory. It also means you don't have to tamper with the base image, which the agent could potentially manipulate…
Jan 2026 · github.com · its alternatives →
- 22

Run Lanes Link as your own personal context MCP: your accounts, memory, skills and secrets behind one endpoint you host, reachable by every AI agent you use.
Sep 2026 · lanes.sh · its alternatives →
- 23MT
https://github.com/mcp-shark/mcp-shark Site: https://mcpshark.sh/ I built MCPShark, a traffic inspector for the Model Context Protocol (MCP). It sits between your editor/LLM client and MCP servers so you can: • See all MCP traffic (requests, responses, tools, resources) in one place • Debug sessions when tools don’t behave as expected • Optionally run “Smart Scan” checks to flag risky tools / configs
Dec 2025 · its alternatives →
- 24

Hi HN! We kept seeing devs get pwned through MCP tools in ways that security scanners completely miss. So we built an open-source analyzer to catch these attacks. Our first OSS by Mighty team. The problem: At Defcon, we saw MCP exploits with 100% success rate against Claude and Llama. Three attack patterns: Hidden Unicode in "error messages" - Paste a colleague's error into Claude, your SSH keys get exfiltrated Trusted tool updates - That database tool you've used for months? Last week's update added credential theft Tool redefinition - Malicious tool redefines "deploy to prod" to run…
2025 · github.com · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →