Kavach MCP Security
Security middleware for AI agents and MCP servers
Kavach MCP Security launched on June 9, 2026 with 3 votes, #6,658 of 22,647 launches that month and more than 50% of that year's launches.
What it does
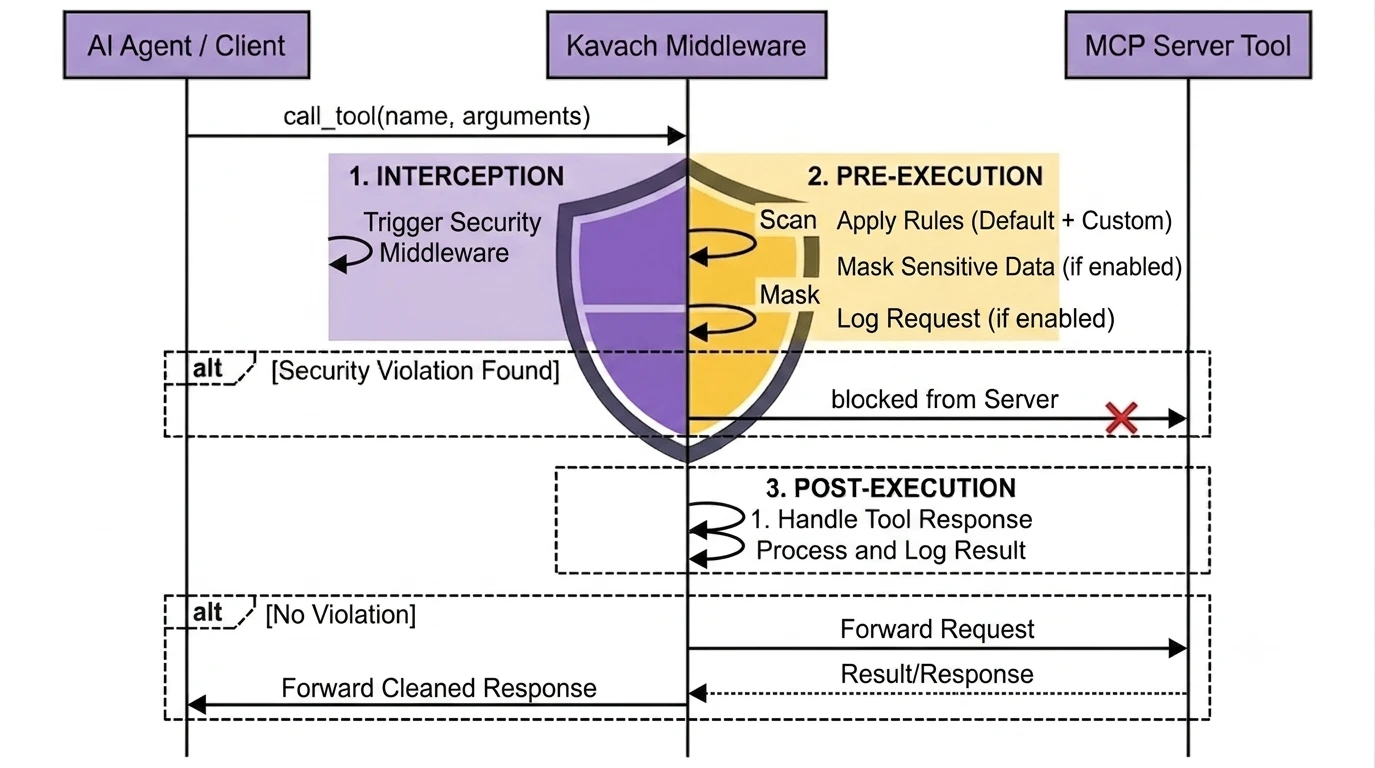
Kavach MCP Security is a security middleware for MCP servers and AI agents. It inspects tool calls before execution to detect prompt injections, secret exposure, sensitive data leaks, and unsafe actions. Developers can enforce security policies, rate limits, tool access controls, and audit logging with minimal code changes. Built for the growing ecosystem of AI agents, MCP servers, APIs, and autonomous workflows.
Does a similar job
all alternatives → Permit MCP GatewayMar 2026 · permit.io · ▲134
Hi HN, Gabriel, Co-Founder at Permit.io. We're releasing Permit MCP Gateway today, an authorization proxy for MCP servers. TL;DR - we built an MCP Gateway that developers love and CISOs trust. Watch more[0] Now, after your little hate on using fancy copy on HN, to the real thing: MCP is in a strange place. Developers are debating whether it's overcomplicated compared to CLIs or skills files. Meanwhile, enterprises are adopting it by default because every agentic system that acts on your behalf, Cursor, Claude, Copilot, internal agents, needs a stable infrastructure for connecting to tools.…
 Risk Analysis Database of Every MCP ServerFeb 2026 · mcp.armor1.ai · ▲22
Hi HN, We’re building security tooling around agentic AI systems. Today, we're releasing our public MCP catalog with detailed risk analysis for every MCP server we've found on the internet: https://mcp.armor1.ai/mcp-directory We all love agents and the power that MCPs unlock: suddenly your AI assistant can query databases, manage files, call APIs, and interact with the real world. But when we started adopting MCPs ourselves, we kept running into the same nagging questions: Is this MCP safe? Where is my data actually going? Could it execute destructive actions? Is it…
 Klavis AI – Open-source MCP integration for AI applications2025 · github.com · ▲79
Hi HN, we are excited to show you Klavis AI. It is an open source project and we provide hosted versions with API access as well. (Website: https://www.klavis.ai/, Github repo: https://github.com/Klavis-AI/klavis) We're addressing a couple of key problems with using MCPs. First, many available MCP servers lack native or used-based authentications, creating security vulnerabilities and adding complexity during development. Second, many MCP servers are personal projects, not designed for the reliability needed in production. Connecting to these servers…
 MCP3602025 · mcp360.ai · ▲61
Hey HN Community, I built MCP360 after spending weeks integrating APIs for an AI agent project. Each tool needed its own setup, auth, billing, and maintenance. When any APIs changed, my integrations broke. I got tired of it. MCP360 is a single gateway giving AI agents access to 100+ tools through one config block. Search engines, web scraping, SEO, e-commerce data, maps, domain tools, and more. Real example: Instead of managing Google Search, web scraping, SERP tracking, and keyword research as 4 separate subscriptions (4 bills, 4 auth systems, 4 points of failure), you connect once. Works…
 MCPGod: Fine-grained control over MCP clients, servers, and tools2025 · github.com · ▲37
Hey everyone, I've wanted an easy way to control which mcp server tools are available to clients. So for example, I might want a gmail server to only expose the read tool (but not send, delete etc). I figured if I create a cli for spawning mcp servers, I could intercept the stdin, stdout, stderr etc and modify what the clients see when they are making calls to list tools, resources, and prompts. Well it worked! In the initial version you can easily add a server to claude with a safe list of tools: npx -y mcpgod add @modelcontextprotocol/server-everything --client claude --tools=echo,add…
 MCP Security Suite2025 · github.com · ▲36
Hi HN! We kept seeing devs get pwned through MCP tools in ways that security scanners completely miss. So we built an open-source analyzer to catch these attacks. Our first OSS by Mighty team. The problem: At Defcon, we saw MCP exploits with 100% success rate against Claude and Llama. Three attack patterns: Hidden Unicode in "error messages" - Paste a colleague's error into Claude, your SSH keys get exfiltrated Trusted tool updates - That database tool you've used for months? Last week's update added credential theft Tool redefinition - Malicious tool redefines "deploy to prod" to run…
More ai this month
the category →


Paintings by AI models: programs run through a simulation of oil paint.
AI · 21d ago · stillwet.art
 PixVerse R2▲381
A real-time world model you can explore and change
AI · 29d ago · world.pixverse.video

Source: Product Hunt launch ↗
Launched alongside, June 2026
the whole month → Fundraisly▲1,537
AI fundraising agent that finds investors and books meetings
AI · Jun 2026 · fundraisly.com
 Homebrew 6.0.0▲1,481
Today, I’m proud to announce Homebrew 6.0.0. The most significant changes since 5.1.0 are a new tap trust security mechanism, the new faster, smaller, default internal Homebrew JSON API, sandboxing on Linux, better defaults informed by our user survey, many brew bundle improvements, improved performance and initial support for macOS 27 (Golden Gate). Happy to discuss any questions here!
Dev tools · Jun 2026 · brew.sh

Hi HN! I was super frustrated at apps like tiktok and wechat preventing me from saving or downloading the animated gifs, so I made a little tool to turn a screen recording into a slack-sized emoji. Hope you get some value from this!
Life & fun · Jun 2026 · vorpus.github.io


Search 18 years of Hacker News and chart how any topic, tool, or person trended. Overlay terms to compare their rise and fall across 45M posts and comments.
Life & fun · Jun 2026 · hackernewstrends.com