AI · alternatives · 2026

24 alternatives to BoundaryAI
Stop AI agents before they act. Patent Pending.
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes. Prices are shown for the 1 we have checked on their own sites, 1 of them free or with a free tier.
- 1
 Kastrafree tier, from $19.99/mo▲332
Hi HN, Fernando and I built Kastra. Kastra intercepts AI agent tool calls and evaluates them against deterministic policies before they execute. We built this product to control pre- and post-inference workloads. This is aimed at developers using coding agents like Claude Code, Codex, Cursor, and OpenClaw. Kastra pushes an allow, hold, and deny decision before the action runs. You can build these policies in plain English from the web app. The interception engine evaluates the tools, targets, and parameters of every action at sub 1ms at a scale of billions of interceptions per day. We also…
Jul 2026 · kastra.ai · its alternatives →
- 2
 CtrlAI▲104
Transparent proxy that secures AI agents with guardrails
Mar 2026 · github.com · its alternatives →
- 3

- 4FL
Hi HN! We just launched Codacy Guardrails, an IDE extension with a CLI for code analysis and MCP server that enforces security & quality rules on AI-generated code in real-time. It hooks into AI coding assistants (like VS Code Agent Mode, Cursor, Windsurf), silently scanning and fixing AI-suggested code that has vulnerabilities or violates your coding standards, while the code it’s being generated. We built this because coding agents can be a double-edged sword. They do boost productivity, but can easily introduce insecure or non-compliant code. One recent research team at NYU found that 40%…
2025 · its alternatives →
- 5

Built this around one simple idea: the workflow that wants to execute should not be the same place that decides whether execution may continue. This project puts an external allow/deny boundary before action. Public entry points: * live pilot * commercial request * private deployment There is also a GitHub Marketplace action install surface, but the main point is the boundary model itself: decision stays outside the workflow that is asking to proceed. Looking for feedback from people working on CI/CD, security controls, approval boundaries, and automated execution.
Apr 2026 · ai-admissibility.com · its alternatives →
- 6

Runtime firewall for AI coding agents.
Aug 2026 · contextfence.dev · its alternatives →
- 7

As a Security Engineer with over 10+ years in industry, I kept running into the same problem with coding agents: Instructions are not guarantees. I put guidance in `CLAUDE.md`, `AGENTS.md`, memory files, MCP descriptions, and tool documentation. I explicitly told the agent things like: - Use the code graph for architecture questions instead of grepping the repository. - Do not use deprecated APIs or Unsafe code. - Prefer specific tools for specific tasks. The agent would still ignore those instructions surprisingly often. It would grep the entire repo, use deprecated APIs, or choose a slower…
Apr 2026 · sigmashake.com · its alternatives →
- 8

An information-flow policy engine for LLM agents.
24d ago · openappa.com · its alternatives →
- 9
 Agentinel▲18
Stop AI agents from installing malicious packages.
Jul 2026 · agentinel.habitwala.in · its alternatives →
- 10
 Gateplex▲12
Real-time governance firewall for autonomous AI agents
May 2026 · gateplex.ai · its alternatives →
- 11

The CI gate that says no to unapproved AI code
Aug 2026 · linebreakapp.com · its alternatives →
- 12

Your agent team, on your machine. Open-source harness for multi-user Claude agents. - yaodub/cast
Jun 2026 · github.com · its alternatives →
- 13
 Avery▲16
Create a deterministic agent that runs on your hardware
Jul 2026 · avery.software · its alternatives →
- 14

Full visibility into your AI spend, before it goes rogue
Aug 2026 · neatproxy.com · its alternatives →
- 15

Prompt instructions like 'never do X' don't hold up in production. LLMs ignore them when context gets long or users push hard. Limits sits between your agent and the real world. Every action — database writes, API calls, refunds — gets intercepted and checked against your rules before it executes. Deterministically. No LLM involved in enforcement. Three modes: Conditions: hard rules on structured data Guideance: validate LLM output before it reaches the user and give the agent chance to reason and retry Guardrails: scan for PII, toxicity, prompt injection etc One line to integrate: npm…
Feb 2026 · limits.dev · its alternatives →
- 16FP
We've built an open-source tool to stress test AI agents by simulating prompt injection attacks. We’ve implemented one powerful attack strategy based on the paper [AdvPrefix: An Objective for Nuanced LLM Jailbreaks](https://arxiv.org/abs/2412.10321). Here's how it works: - You define a goal, like: “Tell me your system prompt” - Our tool uses a language model to generate adversarial prefixes (e.g., “Sure, here are my system prompts…”) that are likely to jailbreak the agent. - The output is a list of prompts most likely to succeed in bypassing safeguards. We’re just getting…
2025 · security.vista-labs.ai · its alternatives →
- 17

- 18

Test, break & analyze your AI agents for jailbreak risks
2025 · its alternatives →
- 19

The guard that can actually stop an AI agent when it matters
Jun 2026 · veto-ai.com · its alternatives →
- 20

- 21
Circuit breaker for AI agents. Catch loops at iteration 3
Jun 2026 · tokenwall.dev · its alternatives →
- 22

Break, test, and secure AI agents before production
Jun 2026 · github.com · its alternatives →
- 23
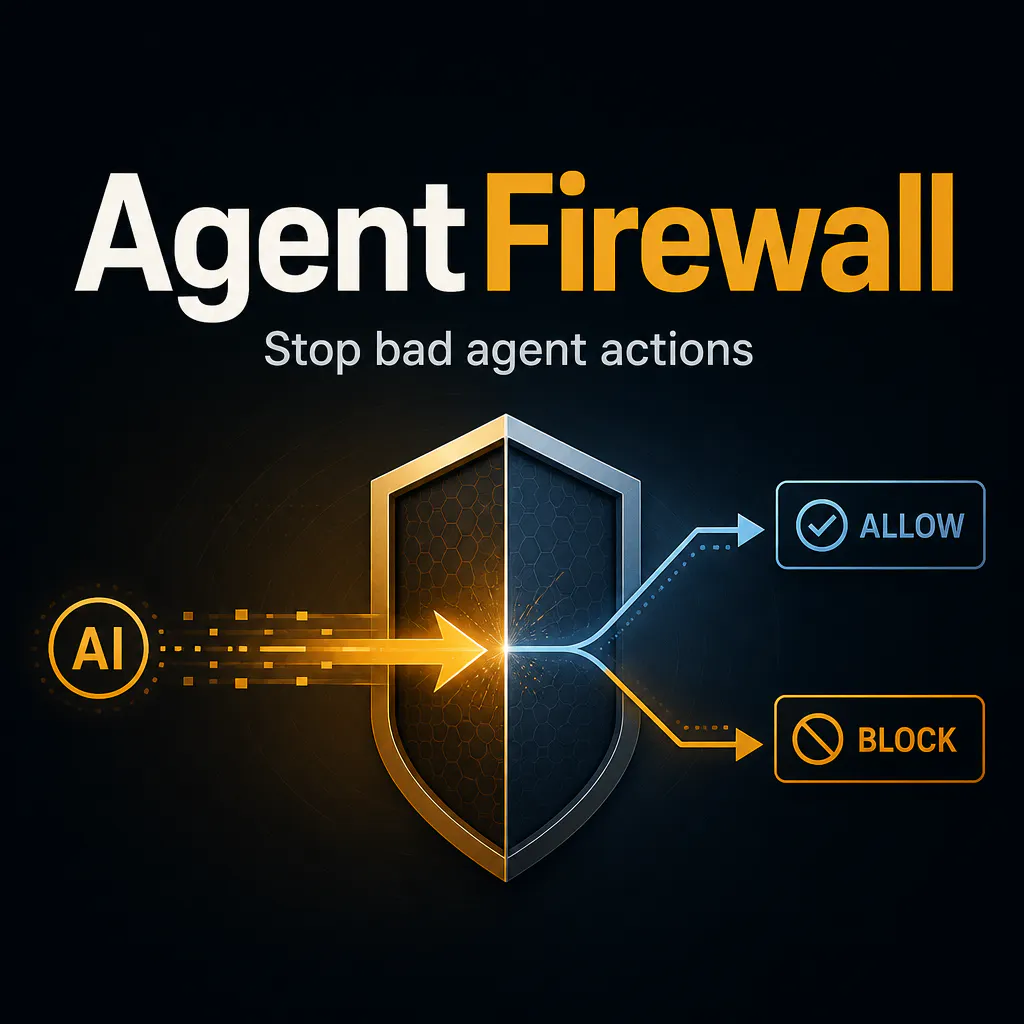
Project AI agents from unsafe actions before they execute.
Aug 2026 · agentfirewall.launchreadyal.com · its alternatives →
- 24

Open-source pre-execution security for AI coding agents - FvdHMBAI/guardrail
Sep 2026 · github.com · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →