Dev tools · alternatives · 2026

24 alternatives to AI Admissibility
Built this around one simple idea: the workflow that wants to execute should not be the same place that decides whether execution may continue. This project puts an external allow/deny boundary before action. Public entry points: * live pilot * commercial request * private deployment There is also a GitHub Marketplace action install surface, but the main point is the boundary model itself: decision stays outside the workflow that is asking to proceed. Looking for feedback from people working on CI/CD, security controls, approval boundaries, and automated execution.
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes. Prices are shown for the 1 we have checked on their own sites, 1 of them free or with a free tier.
- 1
 Kastrafree tier, from $19.99/mo▲332
Hi HN, Fernando and I built Kastra. Kastra intercepts AI agent tool calls and evaluates them against deterministic policies before they execute. We built this product to control pre- and post-inference workloads. This is aimed at developers using coding agents like Claude Code, Codex, Cursor, and OpenClaw. Kastra pushes an allow, hold, and deny decision before the action runs. You can build these policies in plain English from the web app. The interception engine evaluates the tools, targets, and parameters of every action at sub 1ms at a scale of billions of interceptions per day. We also…
Jul 2026 · kastra.ai · its alternatives →
- 2
Fine-Grained Permissions for AI-Powered Applications
2025 · permit.io · its alternatives →
- 3
 Preloop▲121
Hey HN, I’m Yannis, co-founder of Preloop. We’ve built a proxy for the Model Context Protocol (MCP) that lets you add human approval gates to your AI agents without changing your agent code. We’re building agents that use tools (Claude Desktop, Cursor, etc.), but we were terrified to give them write-access to sensitive systems (Stripe, Prod DBs, AWS). We didn't want to rewrite our agents to wrap every tool call in complex "ask_user" logic, especially since we use different agent runtimes. We built Preloop as a middleware layer. It acts as a standard MCP server proxy.You point your agent to…
Jan 2026 · preloop.ai · its alternatives →
- 4

Anthropic and OpenAI's publicly available models are explicitly guard-railed so that they refuse offensive tasks. And their cyber-focussed models are gated for enterprises. This leaves SMEs and mid market open to major vulnerabilities. AI can be used as both an adversarial and defensive tool in the world of cyber. A worst case outcome is if only the adversaries have access. Meanwhile, most existing AI cyber tools are just wrappers. The problem is that they still have all the guardrails on from the foundation model where they will inherit its refusals. For this project we've post-trained a…
Jun 2026 · argusred.com · its alternatives →
- 5
 BoundaryAI ▲1
Stop AI agents before they act. Patent Pending.
May 2026 · boundaryai.ai · its alternatives →
- 6
 Custosa▲15
Permission and compliance layer for Enterprise AI
Mar 2026 · custosa.com · its alternatives →
- 7
- 8

Prompt instructions like 'never do X' don't hold up in production. LLMs ignore them when context gets long or users push hard. Limits sits between your agent and the real world. Every action — database writes, API calls, refunds — gets intercepted and checked against your rules before it executes. Deterministically. No LLM involved in enforcement. Three modes: Conditions: hard rules on structured data Guideance: validate LLM output before it reaches the user and give the agent chance to reason and retry Guardrails: scan for PII, toxicity, prompt injection etc One line to integrate: npm…
Feb 2026 · limits.dev · its alternatives →
- 9

We’ve been building visual rule engines (clear spreadsheet interfaces -> API endpoints that map incoming data to a large number of potential outcomes), and had the fun idea lately to see what happens when we use our decision table UI with Claude’s PreToolUse hook. The result is a surprisingly useful policy/gating layer– these tables let your team: - Write conditional, exception-friendly policies beyond globs/prefixes (e.g. allow rm -rf only in */node_modules/*, deny / or $HOME, ask if --force or network call; gate kubectl delete / SQL DROP with a clear reason) -…
Jan 2026 · github.com · its alternatives →
- 10

Your agent team, on your machine. Open-source harness for multi-user Claude agents. - yaodub/cast
Jun 2026 · github.com · its alternatives →
- 11

An information-flow policy engine for LLM agents.
24d ago · openappa.com · its alternatives →
- 12
Project AI agents from unsafe actions before they execute.
Aug 2026 · agentfirewall.launchreadyal.com · its alternatives →
- 13

The CI gate that says no to unapproved AI code
Aug 2026 · linebreakapp.com · its alternatives →
- 14
 Greywall▲10
Prefix any AI coding agent with `greywall --` for a live feed of every read, write, and connection. Allow by default; ask mode and deny rules opt-in via config. Linux and macOS.
Mar 2026 · greywall.io · its alternatives →
- 15AO
I have spent a long time working in an XP/TDD style, so when AI coding tools became useful enough for real work, I adopted them quickly. The first bottleneck I hit was not code generation, it was verification: AI could write code and tests quickly, but I was still the person reviewing implementations, clicking through flows, checking logs, inspecting database state, and deciding whether the result was actually correct. That pushed me to move validation further left. Before implementation, AI had to produce test plans. After implementation, it had to execute those plans too: drive the…
Mar 2026 · its alternatives →
- 16
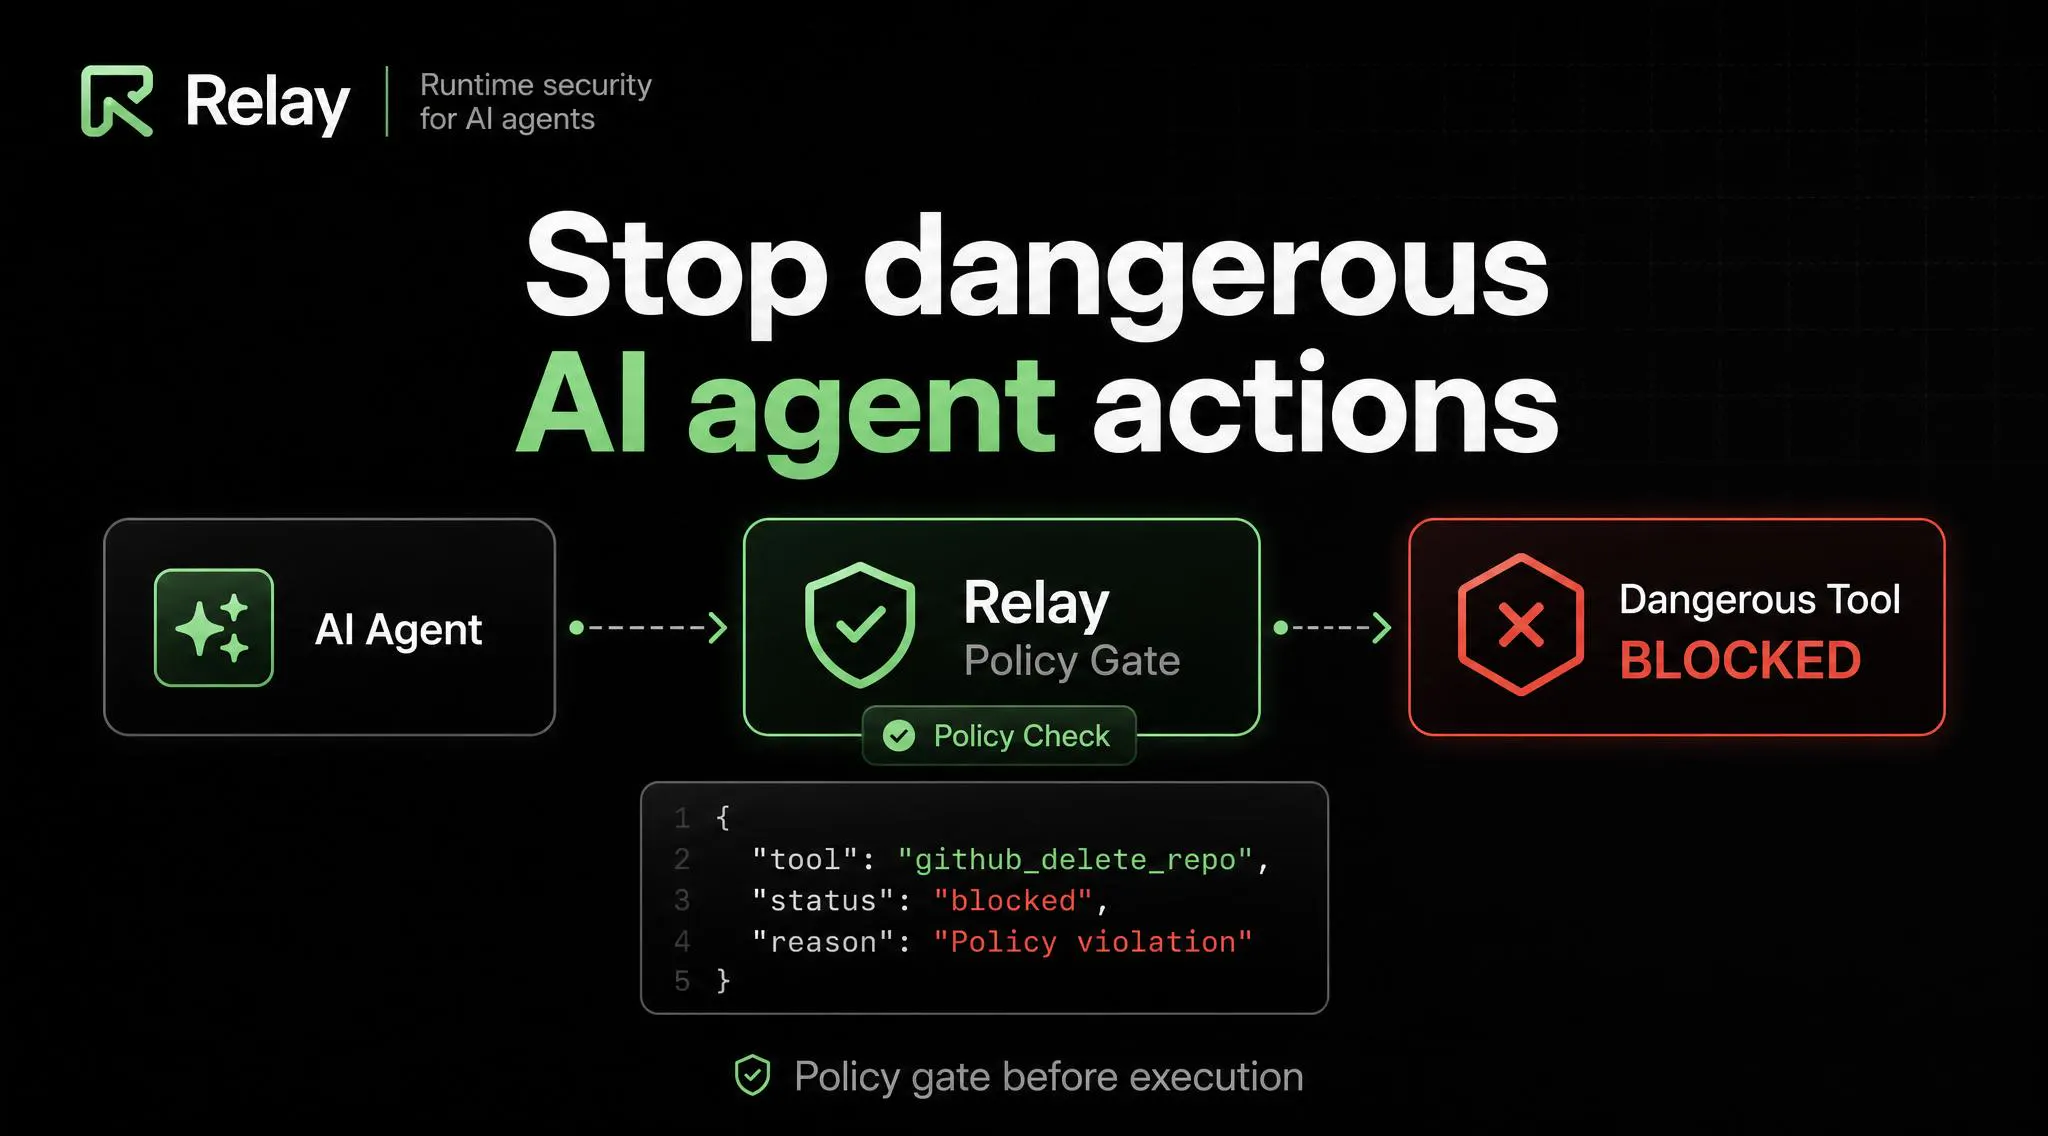
Block dangerous AI agent actions before execution
Jul 2026 · relay-security-lemon.vercel.app · its alternatives →
- 17

In light of recent news about an agent deleting a production database, I thought now would be a good time to share this. As the use of AI tools in production is becoming more common, sadly so will the high profile incidents like the one mentioned. Fewshell is a terminal agent specifically designed to avoid this. There is no setting to enable command auto-approval. This is by-design, so that the user never has to second-guess or worry about accidentally having it enabled. Originally my intention was to build an AI mobile terminal to make typing shell commands easy. But with so many…
Apr 2026 · github.com · its alternatives →
- 18

Hi HN, I’m the creator of Cordum. I’ve been working in DevOps and infrastructure for years (currently in the fintech/security space), and as I started playing with AI agents, I noticed a scary pattern. Most "safety" mechanisms rely on system prompts ("Please don't do X") or flimsy Python logic inside the agent itself. If we treat agents as autonomous employees, giving them root access and hoping they listen to instructions felt insane to me. I wanted a way to enforce hard constraints that the LLM cannot override, no matter how "jailbroken" it gets. So I built Cordum. It’s an open-source…
Jan 2026 · github.com · its alternatives →
- 19

Runtime firewall for AI coding agents.
Aug 2026 · contextfence.dev · its alternatives →
- 20

Your agents spend autonomously. You set the budget, the vendors, and the limits.
May 2026 · arden.sh · its alternatives →
- 21
 OpenVerb▲4
Hi HN, I’ve been working on a project called OpenVerb, which explores an architectural idea for AI systems: separating reasoning from execution. Most AI agent frameworks today focus on improving reasoning loops, planning, and orchestration (LangChain, LangGraph, etc.). But once an agent decides to perform an action, execution usually becomes a direct tool call, script, or API invocation. That approach works, but it also creates some issues: • custom glue code for every integration • inconsistent action schemas • limited determinism in execution • difficult auditing and policy enforcement…
Jul 2026 · openverb.org · its alternatives →
- 22

As a Security Engineer with over 10+ years in industry, I kept running into the same problem with coding agents: Instructions are not guarantees. I put guidance in `CLAUDE.md`, `AGENTS.md`, memory files, MCP descriptions, and tool documentation. I explicitly told the agent things like: - Use the code graph for architecture questions instead of grepping the repository. - Do not use deprecated APIs or Unsafe code. - Prefer specific tools for specific tasks. The agent would still ignore those instructions surprisingly often. It would grep the entire repo, use deprecated APIs, or choose a slower…
Apr 2026 · sigmashake.com · its alternatives →
- 23
 Beacon▲3
Turn 12-month compliance workflows into weeks with AI agents
May 2026 · beaconone.net · its alternatives →
- 24
The AI firewall that understands compliance context
Dec 2025 · promptlock.io · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →