AI · alternatives · 2026
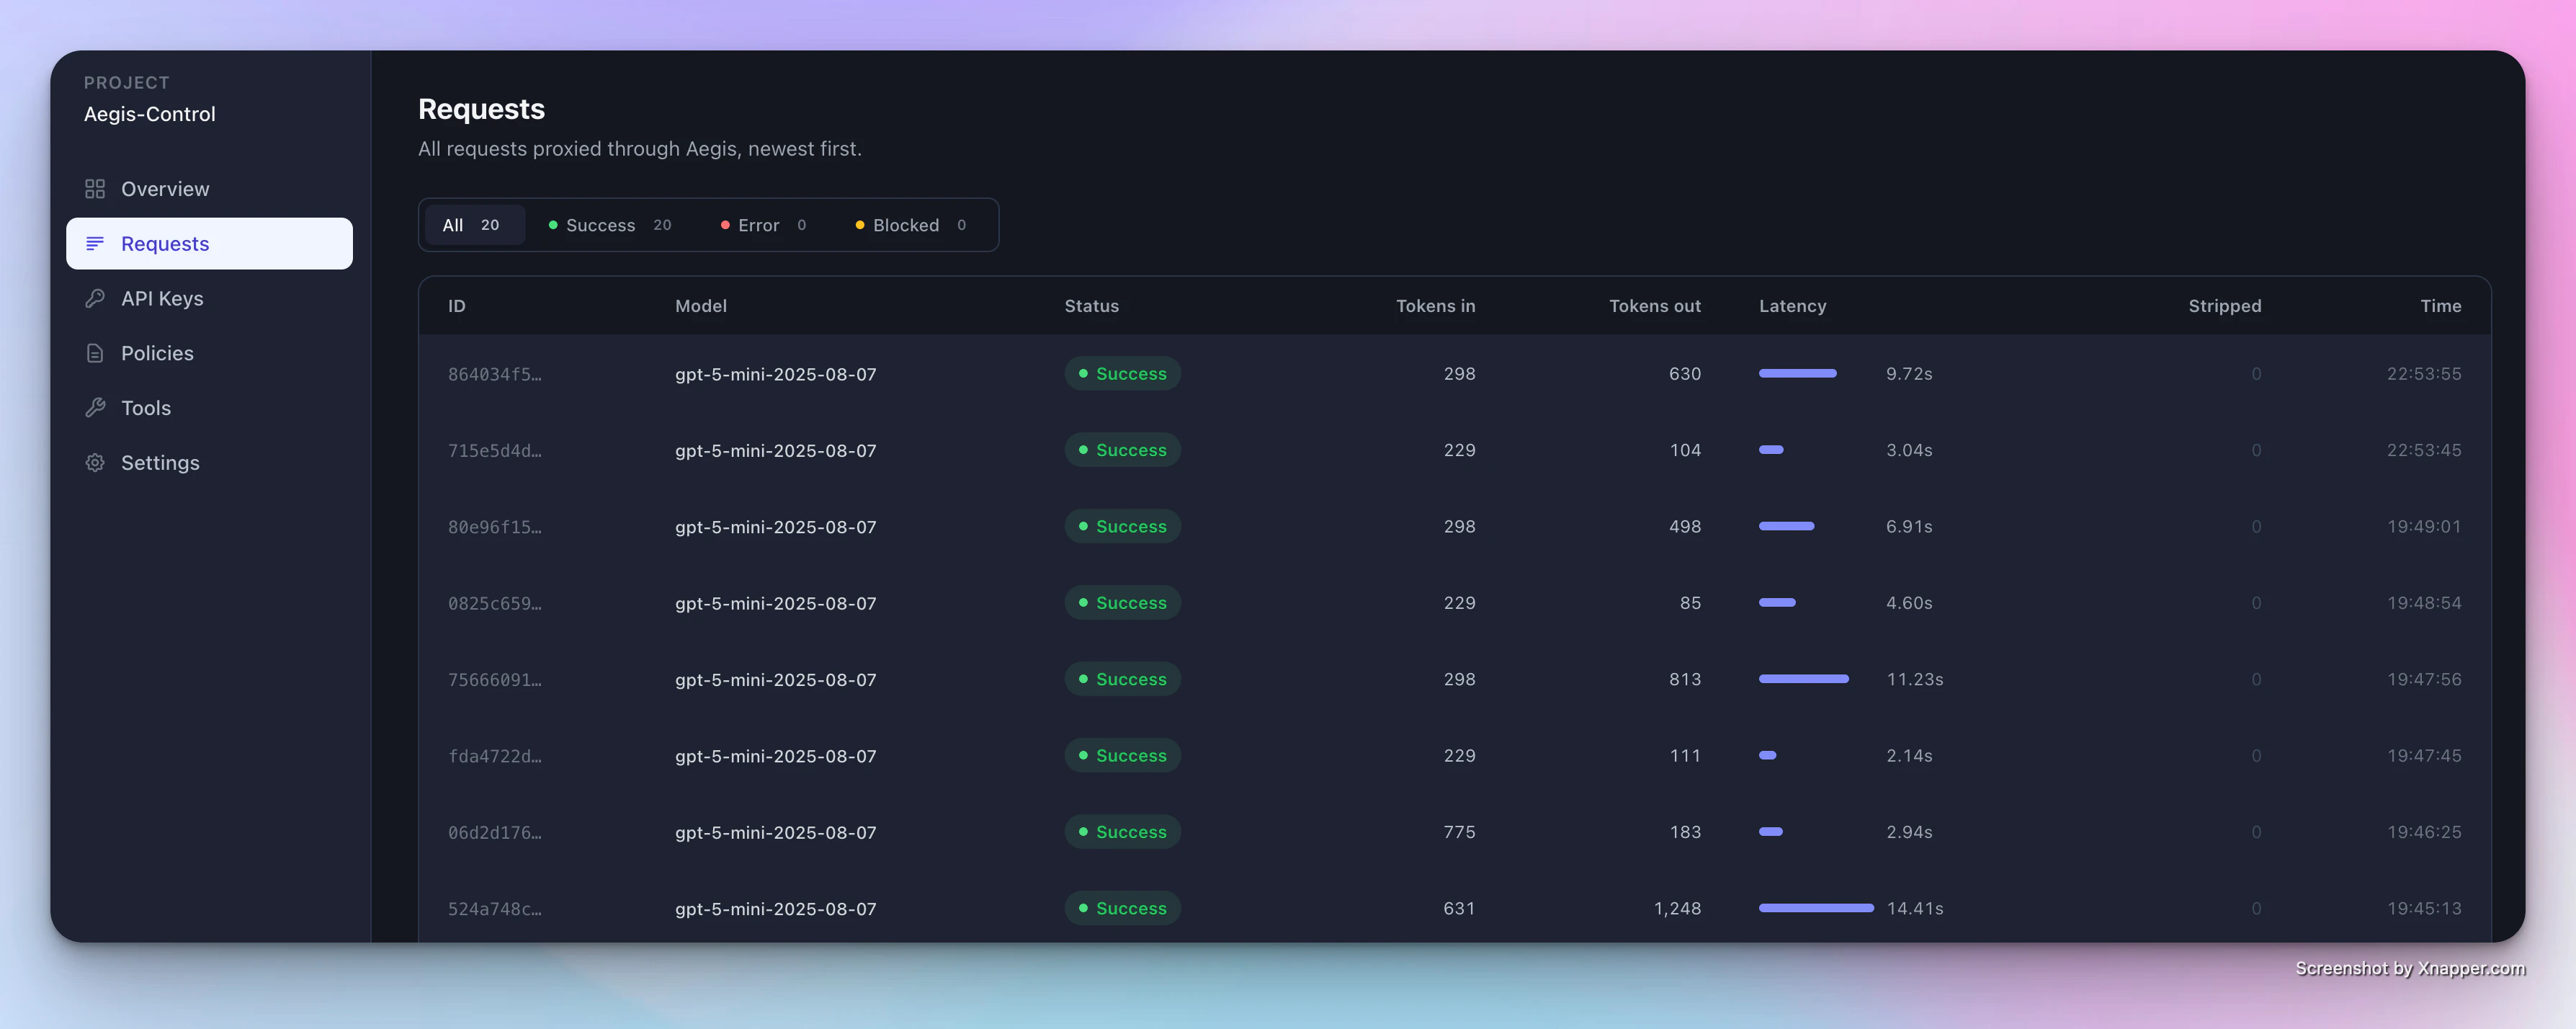
24 alternatives to Aegis-control
Policy enforcement for LLM tool calls.
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1
 Aegisora▲93
The narrow control plane for AI agent tool and API calls.
Aug 2026 · aegisora-ai.vercel.app · its alternatives →
- 2
 LLMWare▲358
Dev tool to make AI apps to deploy privately or locally
2024 · llmware.ai · its alternatives →
- 3
 Arch▲314
Hey HN — I’m Adil from Katanemo (with Salman, Shuguang, and Meiyu) We previously shared an early version of this project as ArchGW. Based on customer feedback, the scope expanded from “LLM routing and model access” into something broader: delivery infrastructure for agentic applications. We renamed it to Plano and reworked the architecture accordingly. The problem On-the-ground AI practitioners will tell you that calling an LLM is not the hard part. The really hard part is delivering agentic applications to production quickly and reliably, then iterating without rewriting system code every…
2024 · github.com · its alternatives →
- 4

Many teams connecting LLMs to external tools eventually encounter the same architectural issue: as more tools and agents are added, the integration pattern becomes an N×M mesh of direct connections. Each agent implements its own auth, retries, rate limiting, and logging; each tool needs credentials distributed to multiple places and observability becomes fragmented. We built LLM gateway with this goal to provide a single place to manage authentication, authorization, routing, and observability for MCP servers, with a path toward a more general agent-gateway architecture in the future. The…
Dec 2025 · truefoundry.com · its alternatives →
- 5
 AEGIS▲2
Open-source LLM defense that publishes its real bypass rate
Aug 2026 · defenseaegis.org · its alternatives →
- 6

- 7

Hi HN, Matvey, Ildar, Joey, and Dominik here. If you're building LLM agents that use tools, you're probably worried about prompt injection attacks that can hijack those tools. We were too, and found that solutions like prompt-based filtering or secondary "guard" LLMs can be unreliable. Our thesis is that agent security should be handled at the network level between the agent and the LLM, just like a traditional web application firewall. So we built Archestra Platform: an open-source gateway that acts as a secure proxy for your AI agents. It's designed to be a deterministic firewall against…
2025 · archestra.ai · its alternatives →
- 8
 CtrlAI▲104
Transparent proxy that secures AI agents with guardrails
Mar 2026 · github.com · its alternatives →
- 9
 Trails▲81
Hey all, Justin here. I previously built Phind, the AI search engine for developers. One of the biggest problems we had there was figuring out what went wrong with bad searches. We had tons of searches per day, but less than 1% of users gave any explicit feedback. So we were either manually digging through searches or making general system improvements and hoping they helped. This problem gets harder with agents. Traces are longer and more complex. It takes more effort to review them, so I'm building a tool that lets you analyze LLM outputs directly to help developers of LLM apps and agents…
Jan 2026 · trails-red.vercel.app · its alternatives →
- 10
 Aegisure▲5
Control & audit layer for your AI coding agents
Jun 2026 · aegisure.dev · its alternatives →
- 11

Prompt instructions like 'never do X' don't hold up in production. LLMs ignore them when context gets long or users push hard. Limits sits between your agent and the real world. Every action — database writes, API calls, refunds — gets intercepted and checked against your rules before it executes. Deterministically. No LLM involved in enforcement. Three modes: Conditions: hard rules on structured data Guideance: validate LLM output before it reaches the user and give the agent chance to reason and retry Guardrails: scan for PII, toxicity, prompt injection etc One line to integrate: npm…
Feb 2026 · limits.dev · its alternatives →
- 12

Hey HN – I built a framework called Aegis to govern AI-assisted software development. The core idea is that AI-generated code should follow the same rules as human code: versioned, validated, observable. Aegis enforces this through blueprint-based development, drift detection, and runtime compliance systems. It’s designed for teams using tools like Copilot, Kilo, or Lovable to build production systems with confidence. This isn’t a library — it’s a way to architect AI-native engineering workflows. Would love feedback, questions, and critiques. Especially curious if others are facing similar…
2025 · github.com · its alternatives →
- 13
- 14
 Argmin AI▲32
Hey, HN community! We've built Argmin AI after shipping LLM features where the demo worked, then the bill and latency got unpredictable in production. Prompts expanded, context grew, retrieval got noisy, retries appeared, and agent workflows added loops. Argmin AI optimizes LLM-related expenses as a system: 1. prompt and context efficiency 2. model selection and routing 3. RAG inefficiencies and caching opportunities 4. agent workflows (tool calls, retries, loop control) Changes are validated with evals and guardrails (tests, gates, judges), tailored to your quality definition and goals.…
Jul 2026 · argminai.com · its alternatives →
- 15

An information-flow policy engine for LLM agents.
23d ago · openappa.com · its alternatives →
- 16
 AEGIS▲4
Self-hosted AI agents that interrupt you less
Jul 2026 · hikmahtechnologies.com · its alternatives →
- 17

AI/LLM Driven Security Camera Agent on your MAC/PC for free
Feb 2026 · sharpai.org · its alternatives →
- 18

New ways of breaking app-integrated LLMs . Contribute to greshake/llm-security development by creating an account on GitHub.
2023 · github.com · its alternatives →
- 19
Agent Aegis is an autonomous multi-agent system that audits.
Nov 2025 · agent-aegis-497122537055.us-west1.run.app · its alternatives →
- 20

We're excited to launch compliant-llm: an open-source toolkit that helps infosec and compliance teams audit AI agents against regulatory frameworks like NIST AI RMF, ISO 42001, and OWASP Top 10. Infosec and compliance teams are now responsible for tracking security and compliance risks of a growing number of AI agents across external and internal apps and third-party vendors. compliant-llm gives you a way to: - Define and run comprehensive red-teaming tests for AI agents - Maps test outcomes to compliance frameworks like NIST AI RMF - Generate detailed audit logs and documentation -…
2025 · github.com · its alternatives →
- 21GL
I wanted to do a complete audit of my AWS account but was dissatisfied with the existing tools. Many of them are clunky to use, and their verbose scan outputs are difficult to understand. So, I built my own open-source tool that uses LLMs to summarize the scan results.
2024 · guard.dev · its alternatives →
- 22

Zero-trust proxy & escalation boundary for AI agents.
Aug 2026 · github.com · its alternatives →
- 23

Governed LLM traffic with verifiable audit evidence
Aug 2026 · github.com · its alternatives →
- 24
Autonomous AI agents for ethical hacking and cyber defense.
2025 · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →