AI · alternatives · 2026

24 alternatives to Causal Safety Engine
Hi HN, this is a safety-first causal engine I’ve been working on. The goal is not to discover more causal relations, but to prevent AI systems from acting when causal signals are unstable, biased, or unsafe. The engine: - runs multi-pass causal analysis - allows safe abstention (no insight is a valid outcome) - includes stability and release-gate tests - is designed to block decisions by default unless causality is robust I’m sharing this mainly to get technical feedback on: - the safety assumptions - the stability criteria - whether this approach makes sense for AI agents / enterprise…
Below are 24 products that do a similar job, ranked by how close each is in meaning and then by launch-day votes.
- 1
 Fluxix▲18
Control what your AI agents can access, run, and spend
4d ago · fluxix.ai · its alternatives →
- 2
 Spec27▲34
Hi HN! We’re a team of ML validation specialists and we’ve been building /Spec27, a tool for testing whether AI agents still do their job safely and reliably as models, prompts, tools, and surrounding systems change. We started working on this because a lot of current LLM evaluation work seems aimed at scoring general model behavior, while many teams are deploying systems that have a specific mission to fulfill. Many of the tools also assume you have full access to the agent stack and traces so you can place SDKs and Gateways, but a lot of agents are being created on vendor platforms…
Apr 2026 · spec27.ai · its alternatives →
- 3

- 4

Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of duties, and cryptographically signed, offline-verifiable audit logs. - makerchecker/MakerChecker
Jul 2026 · github.com · its alternatives →
- 5

Open Source Reliability Harness: Make your agents follow rules. One line of code to enforce, trace, and improve. - GitHub - open-bias/open-bias: Open Source Reliability Harness: Make your agents follow rules. One line of code to enforce, trace, and improve.
Apr 2026 · github.com · its alternatives →
- 6
 RiskKernel▲25
Deterministic cost / loop / time budgets · full observability · crash-resumable runs · human-approval gates · a memory you own. Self-hosted. Your keys. No telemetry. Point it at your existing agents - one env var. - prashar32/riskkernel
Jun 2026 · github.com · its alternatives →
- 7

Hi HN, We’re building security tooling around agentic AI systems. Today, we're releasing our public MCP catalog with detailed risk analysis for every MCP server we've found on the internet: https://mcp.armor1.ai/mcp-directory We all love agents and the power that MCPs unlock: suddenly your AI assistant can query databases, manage files, call APIs, and interact with the real world. But when we started adopting MCPs ourselves, we kept running into the same nagging questions: Is this MCP safe? Where is my data actually going? Could it execute destructive actions? Is it…
Feb 2026 · mcp.armor1.ai · its alternatives →
- 8

A practical guide to building safety layers for AI agents
Aug 2026 · krishhna7.gumroad.com · its alternatives →
- 9BY
Hi HN. We launched a free AI Coding Risk Assessment tool to help engineering teams and businesses benchmark the security and compliance posture of their AI coding workflows and policies against peers in the industry. This anonymous 24-question survey delivers: - A 0–100 risk score that measures your AI coding security posture - A live benchmark that compares your AI-assisted development practices with peers - A research-based checklist that identifies improvement areas We're seeing more and more clients signal their concerns about the sudden increase of source code written by AI coding…
Nov 2025 · its alternatives →
- 10

Enterprise Zero-Trust Security, Cascading Delegation, Human Approvals & Verifiable Audit Infrastructure for Autonomous AI Agents - SRN0129/Agenttrust
2d ago · github.com · its alternatives →
- 11

Research-grounded, harness-agnostic skills for AI coding agents - SteveVitali/agent-skills
Aug 2026 · github.com · its alternatives →
- 12

An empirical validation of physics-inspired runtime monitoring for multi-turn LLM agents across 3,175 total runs spanning four benchmarks (τ³-bench, SWE-bench, MINT, custom local-model battery). A 5-condition ablation study with multi-trial validation (333 SWE-bench runs) demonstrates that Lyapunov
Jun 2026 · github.com · its alternatives →
- 13
Project AI agents from unsafe actions before they execute.
Aug 2026 · agentfirewall.launchreadyal.com · its alternatives →
- 14
- 15
 riskline▲1
Open-source EU AI Act risk engine, deterministic & auditable
Aug 2026 · new-world-coder.github.io · its alternatives →
- 16
Paste a policy doc, get an auditable decision engine
Jul 2026 · ai-rete-rag.com · its alternatives →
- 17

Prompt instructions like 'never do X' don't hold up in production. LLMs ignore them when context gets long or users push hard. Limits sits between your agent and the real world. Every action — database writes, API calls, refunds — gets intercepted and checked against your rules before it executes. Deterministically. No LLM involved in enforcement. Three modes: Conditions: hard rules on structured data Guideance: validate LLM output before it reaches the user and give the agent chance to reason and retry Guardrails: scan for PII, toxicity, prompt injection etc One line to integrate: npm…
Feb 2026 · limits.dev · its alternatives →
- 18LO
Latch is an open-source proxy that sits between AI agents and the tools they use. It intercepts all tool calls and applies security policies in real-time: Safe operations pass through instantly. Risky operations require human approval via dashboard or Telegram. Dangerous operations are blocked completely I built Latch to address the growing security risks of AI agents accessing critical systems. There have been 1,800+ exposed agent gateways discovered in the wild and recent security audits showing multiple vulnerabilities in agent frameworks, so this was motivated by the clear urgent need…
Feb 2026 · latchagent.com · its alternatives →
- 19

AI agents now have impressive reasoning capabilities. This raises an important question: how dangerous are these AI agents at identifying & exploiting web vulnerabilities? We created CVE-bench to find out (I'm one contributor of 16). To our knowledge CVE-bench is the first benchmark using real-world web vulnerabilities to evaluate AI agents' cyberattack capabilities. We included 40 CVEs from NIST's database, focusing on critical-severity vulnerability (CVSS > 9.0). To properly evaluate agents’ attacks, we built isolated environments with containerization and identified 8 common attack…
2025 · github.com · its alternatives →
- 20

Tamper-evident evidence and verification layer for AI agents. Verify any agent's session offline with just openssl. No cloud, no lock-in. - radotsvetkov/akmon
May 2026 · github.com · its alternatives →
- 21
- 22
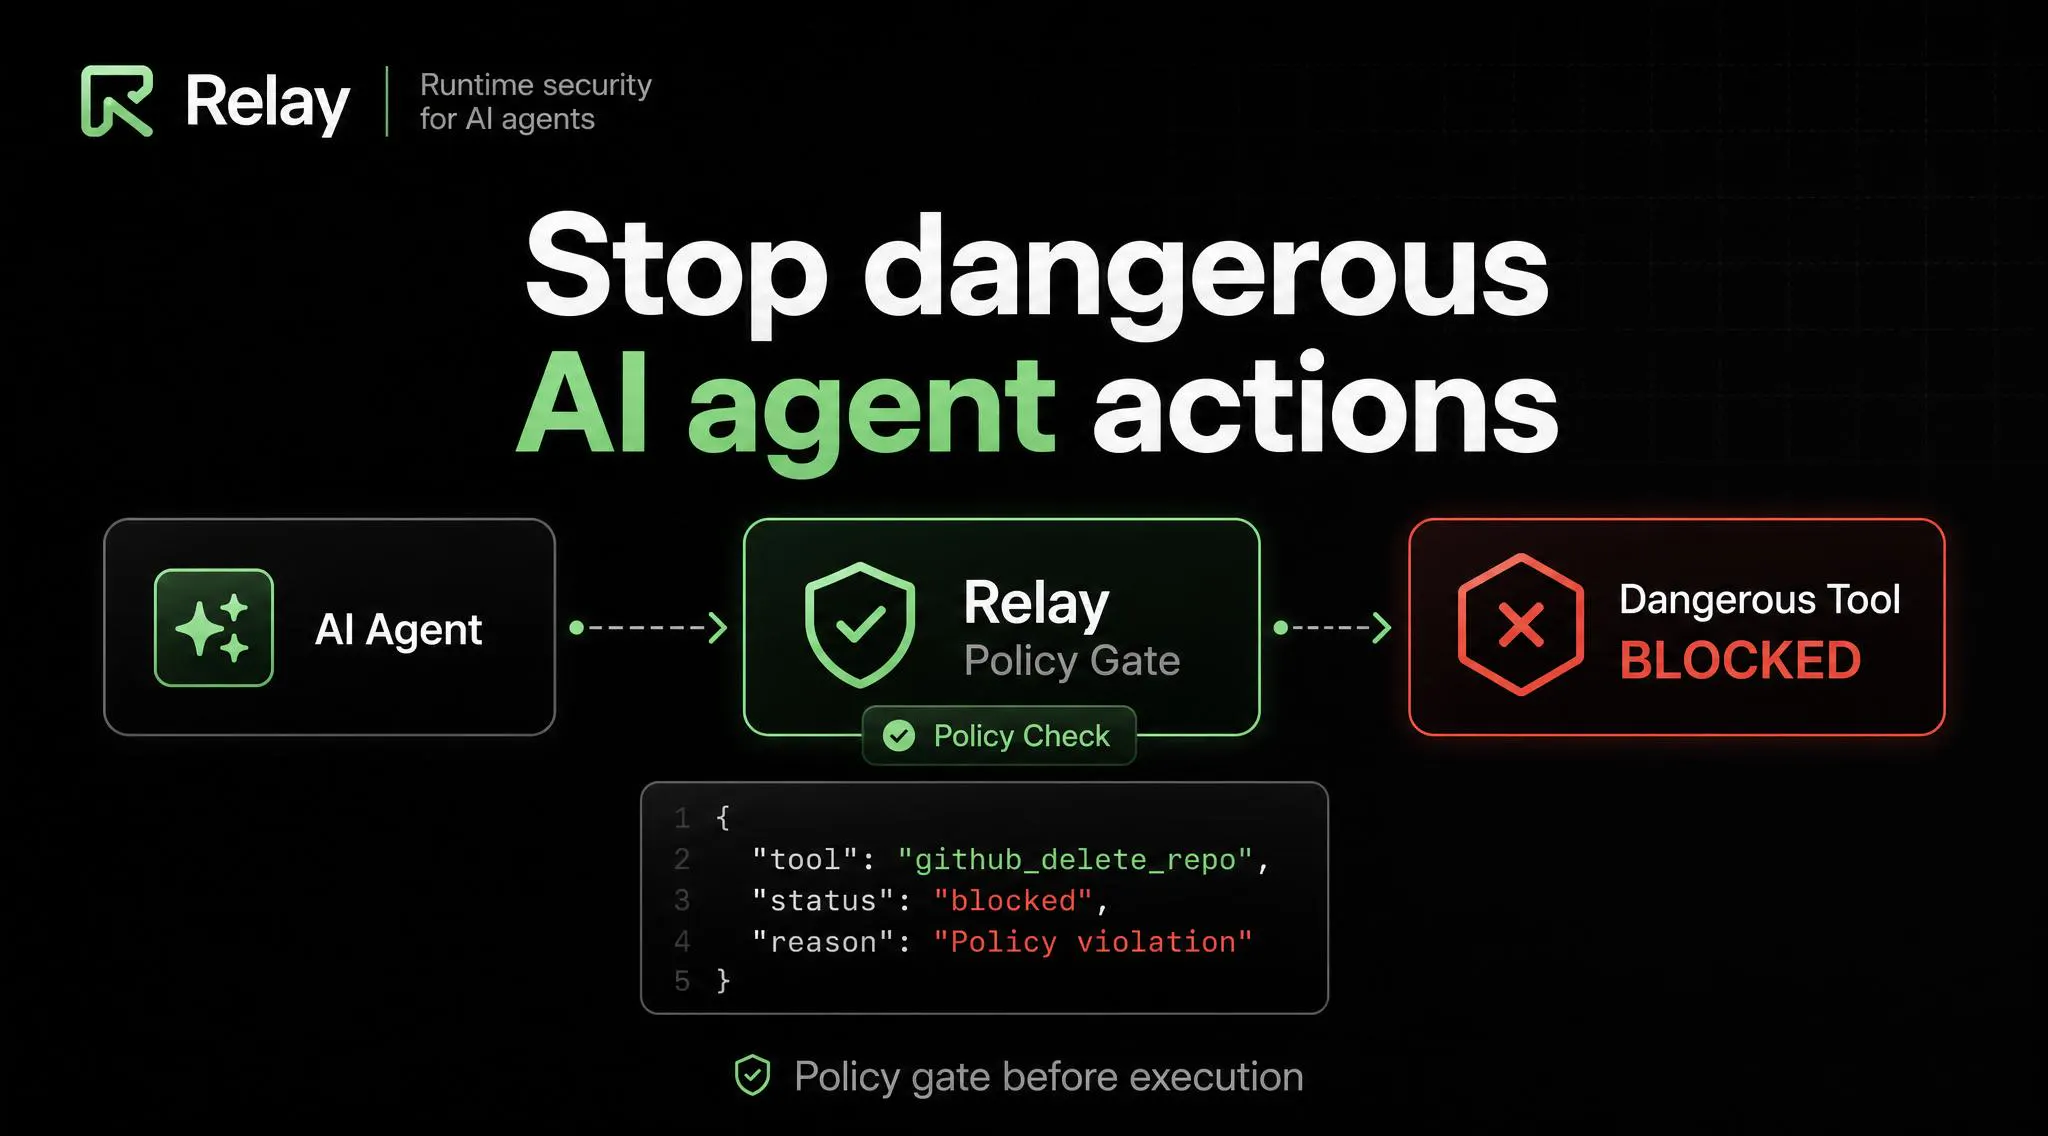
Block dangerous AI agent actions before execution
Jul 2026 · relay-security-lemon.vercel.app · its alternatives →
- 23
Block malicious web content before it reaches your AI.
Jan 2026 · its alternatives →
- 24

anticipate, isolate, neutralize.”
Nov 2025 · black-swan-resilienc-kk7h.bolt.host · its alternatives →
Also compare
Ranked by how close each launch is in meaning, then by votes. Prices were read from each product’s own site when checked and can change. Refine with your own description →